Vulnerability Scanner & Patch Management
Vulnerability scanner and compliance management for your servers, workstations, and virtual machines (VMs). Agent-based or agentless scanning, compliance assessment based on CIS Benchmarks, and integrated patch management. On-premise or SaaS deployment.
The challenge: managing heterogeneity
Infrastructure heterogeneity
Hundreds of technologies to inventory and secure: Windows and Linux servers, workstations, network equipment, hypervisors, databases, middleware...
Technological silos
Disparate tools (SIEM, EDR, configuration management) without cross-functional visibility. No correlation between vulnerabilities and actual configuration.
Wasted time
Manual data collection, reconciling fragmented information, and tedious audits. Risks are evolving faster than your ability to respond.
attack surface
Attack Surface Management
Automatically discover all your IT assets using over 50 specialized connectors.
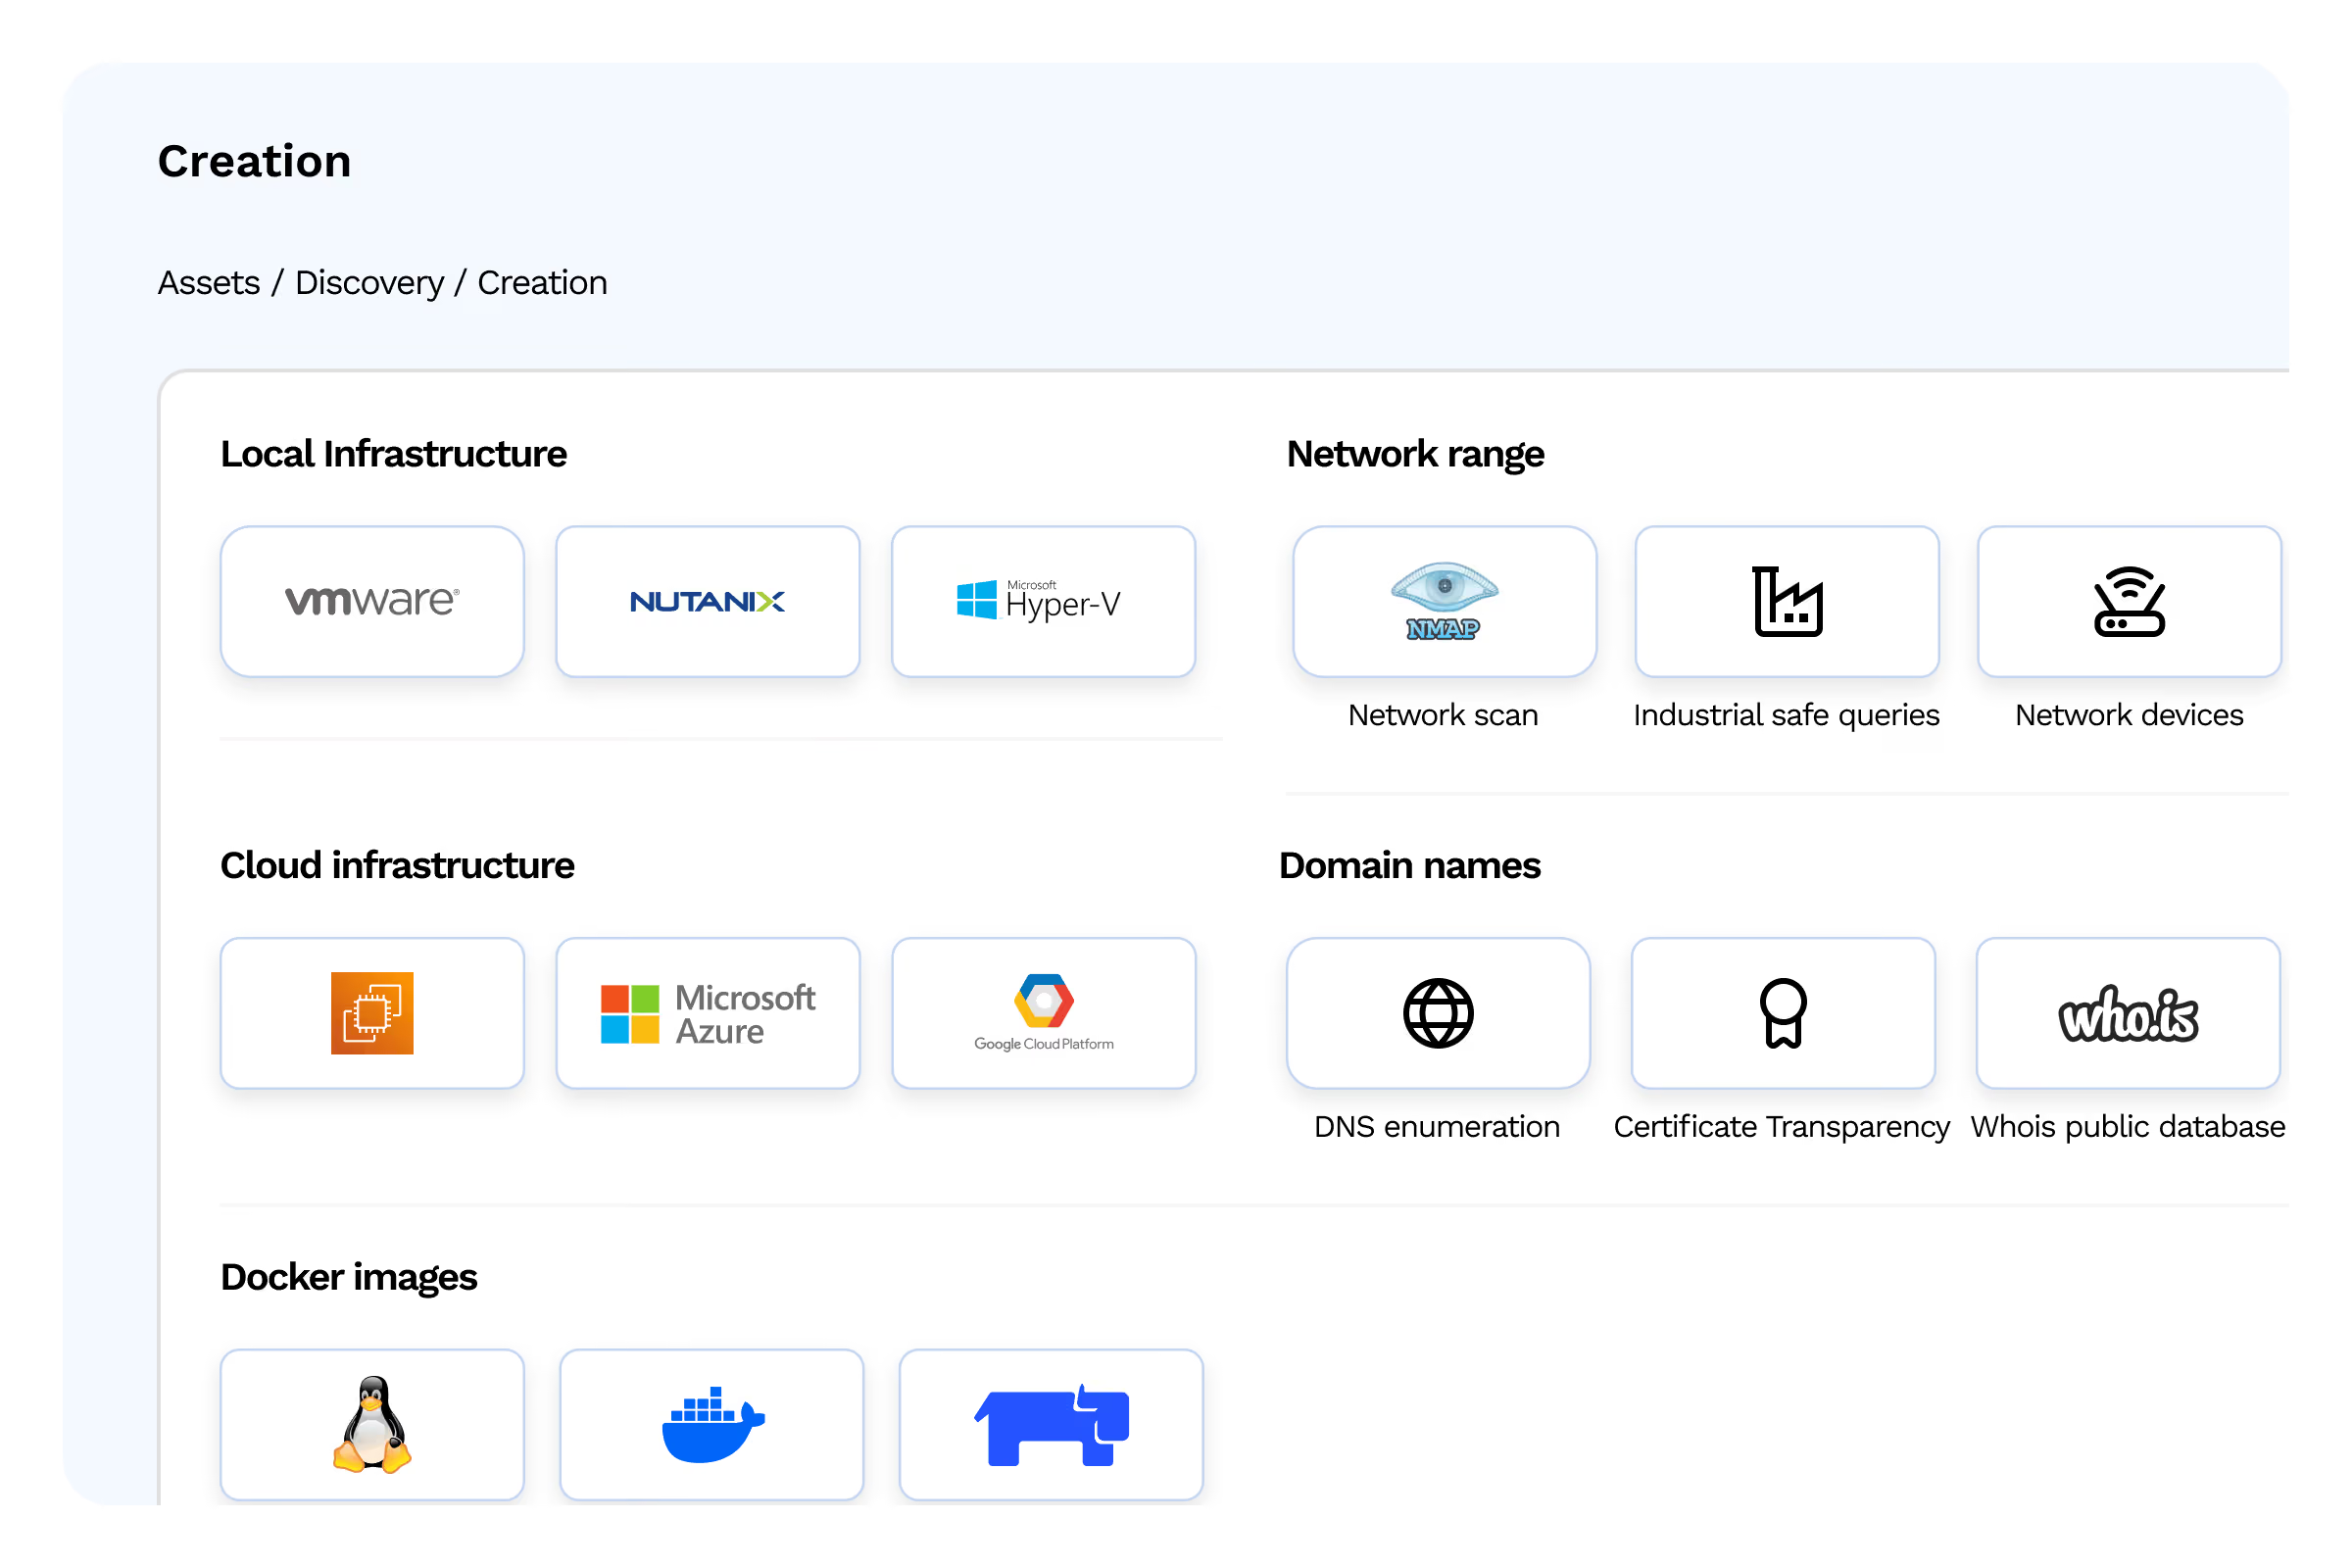
Agent mode
Deployment on every workstation for complete visibility and real-time data
- Item 1
- Item 2
- Item 3
Agentless mode
Authenticated scanning via WinRM/SSH/SNMP for sensitive, network, or ephemeral devices
- Item 1
- Item 2
- Item 3
Offline mode
Import via CSV/JSON files for isolated or air-gapped assets
Import via CycloneDX/SPDX SBOM files
- Item 1
- Item 2
- Item 3
Comprehensive coverage
Servers, workstations, hypervisors, databases, middleware, network equipment
- Item 1
- Item 2
- Item 3
A solid foundation for all your downstream security processes.
Vulnerabilities
Vulnerability Management
Continuous CVE detection, vulnerability prioritization based on risk level, and real-time alerts for critical flaws.
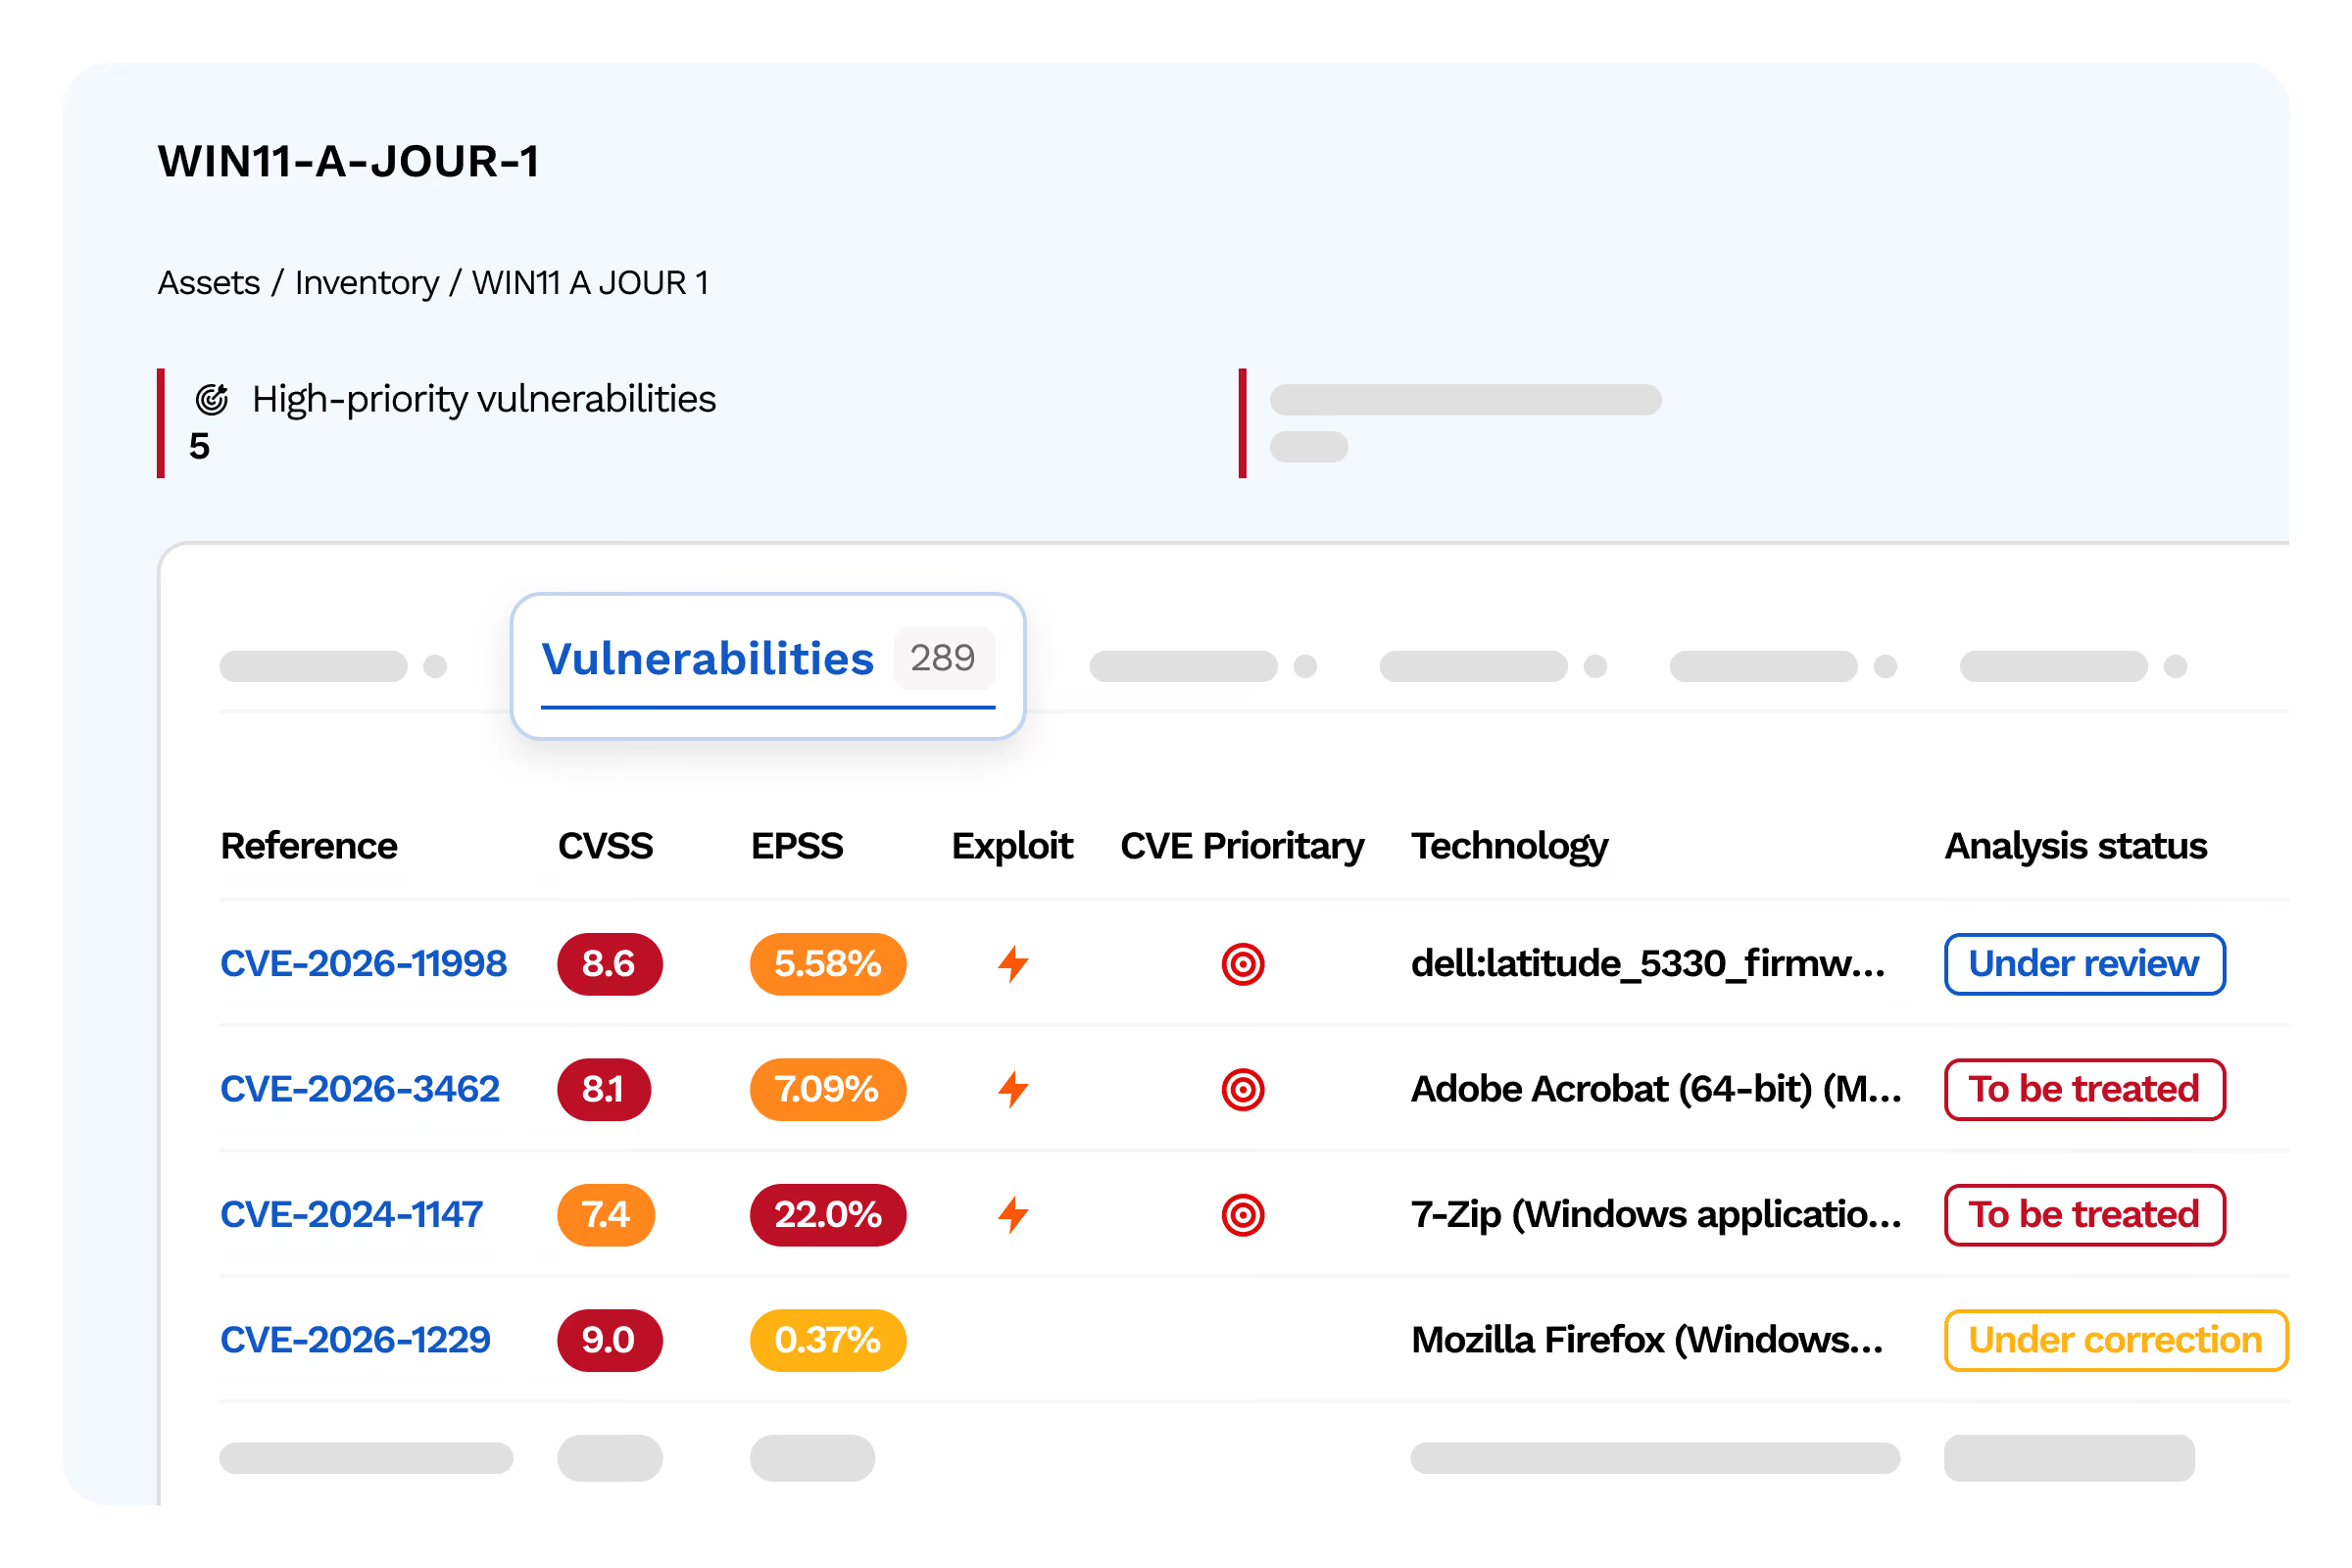
CVE Updates
Hourly feed of new vulnerabilities, MTTD < 1 hour
- Item 1
- Item 2
- Item 3
CVSS-BTE + EPSS Prioritization
Beyond CVSS scores: integrate operational context and exploit probabilities
- Item 1
- Item 2
- Item 3
CERT Alerts
Immediate notifications for critical vulnerabilities (CISA KEV, CERT-FR)
- Item 1
- Item 2
- Item 3
Contextual correlation
Link every CVE to your exposed assets and configurations
- Item 1
- Item 2
- Item 3
Cut through the noise: patch only what matters.
Compliance
Configuration Management
Continuously assess your compliance with security and hardening benchmarks, internal policies, and industry-specific standards.
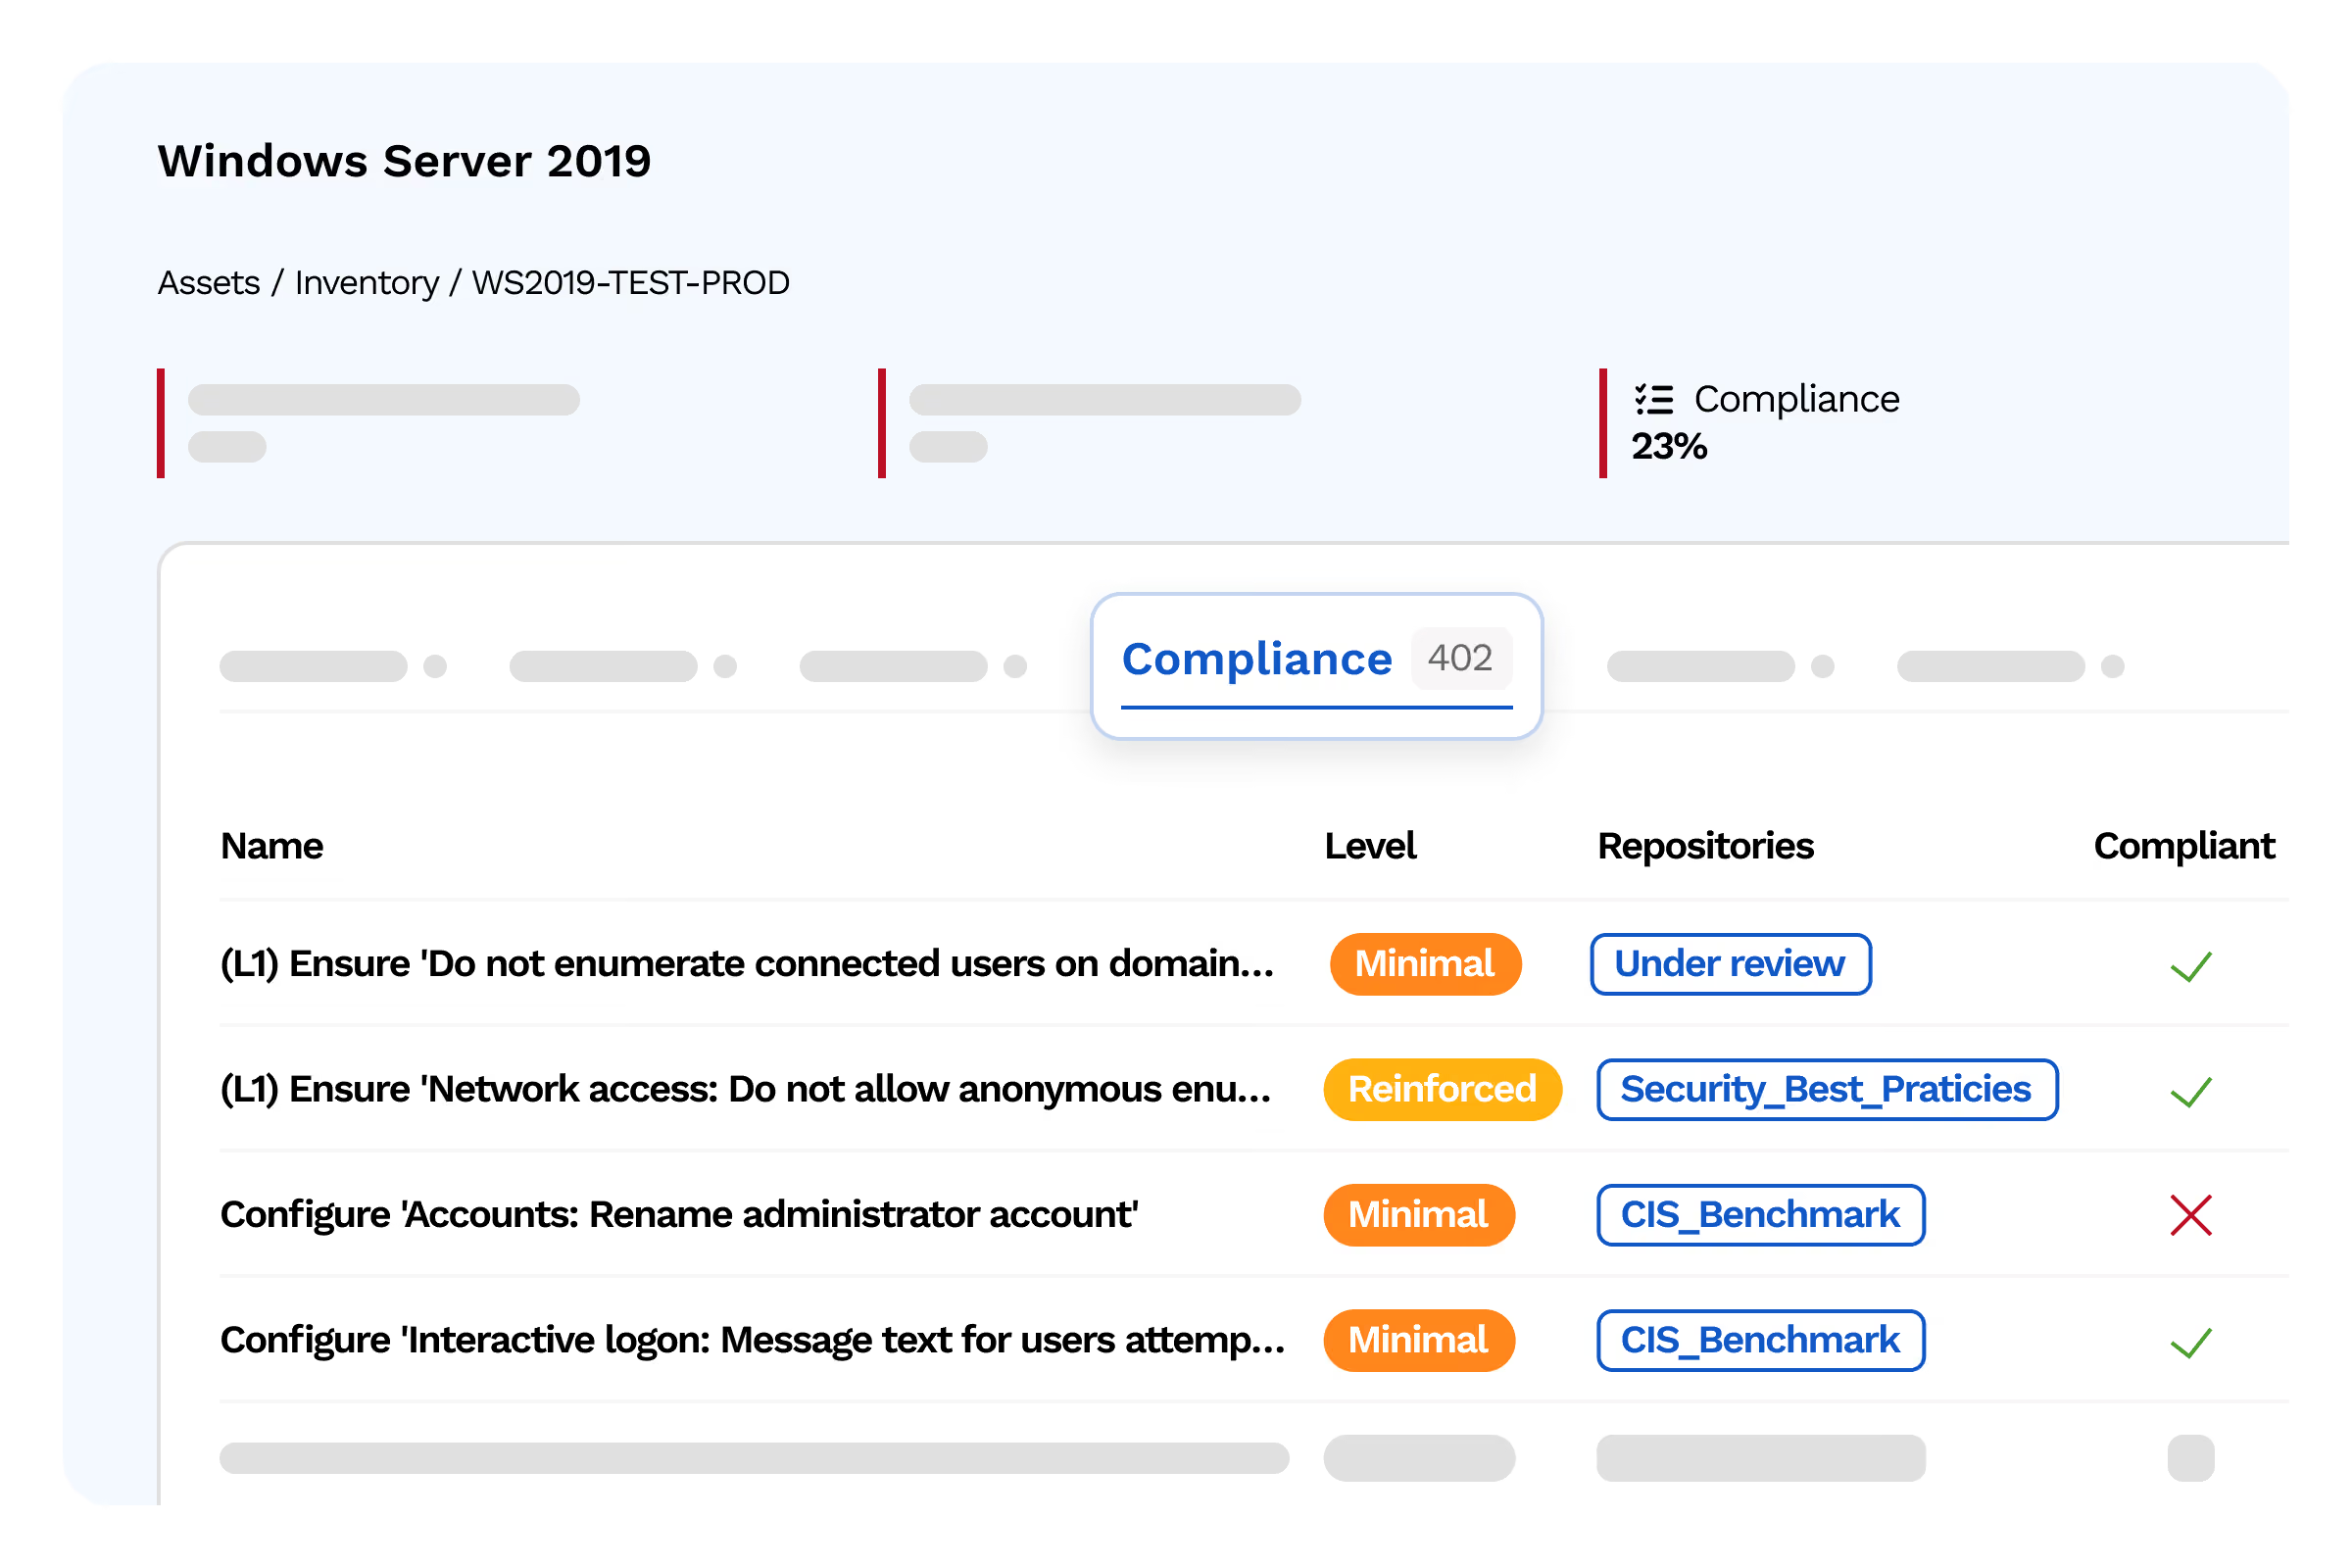
CIS Benchmarks
CIS controls for Windows, Linux, and cloud services
- Item 1
- Item 2
- Item 3
ANSSI/CERT-FR Guides
French applicability: sector-specific recommendations and geopolitical risks
- Item 1
- Item 2
- Item 3
Custom rules
Integration of your internal standards and industry regulations (PCI-DSS, HIPAA, etc.)
- Item 1
- Item 2
- Item 3
Continuous compliance scoring
Real-time dashboard with automatic detection of deviations from the validated baseline
- Item 1
- Item 2
- Item 3
Configuration is your passive defense: keep it tight.
microsoft 365
Microsoft 365 / Entra ID
Audit identities, access, and data sharing at the heart of your Microsoft ecosystem.
Conditional access
Policy analysis and identity spoofing risk
MFA & guest management
MFA coverage, external access audit, and bypass risks
SharePoint/Teams/OneDrive sharing
Detect accidental public sharing and faulty access controls
Exchange anti-phishing
Anti-phishing policies, transport rules, and log compliance
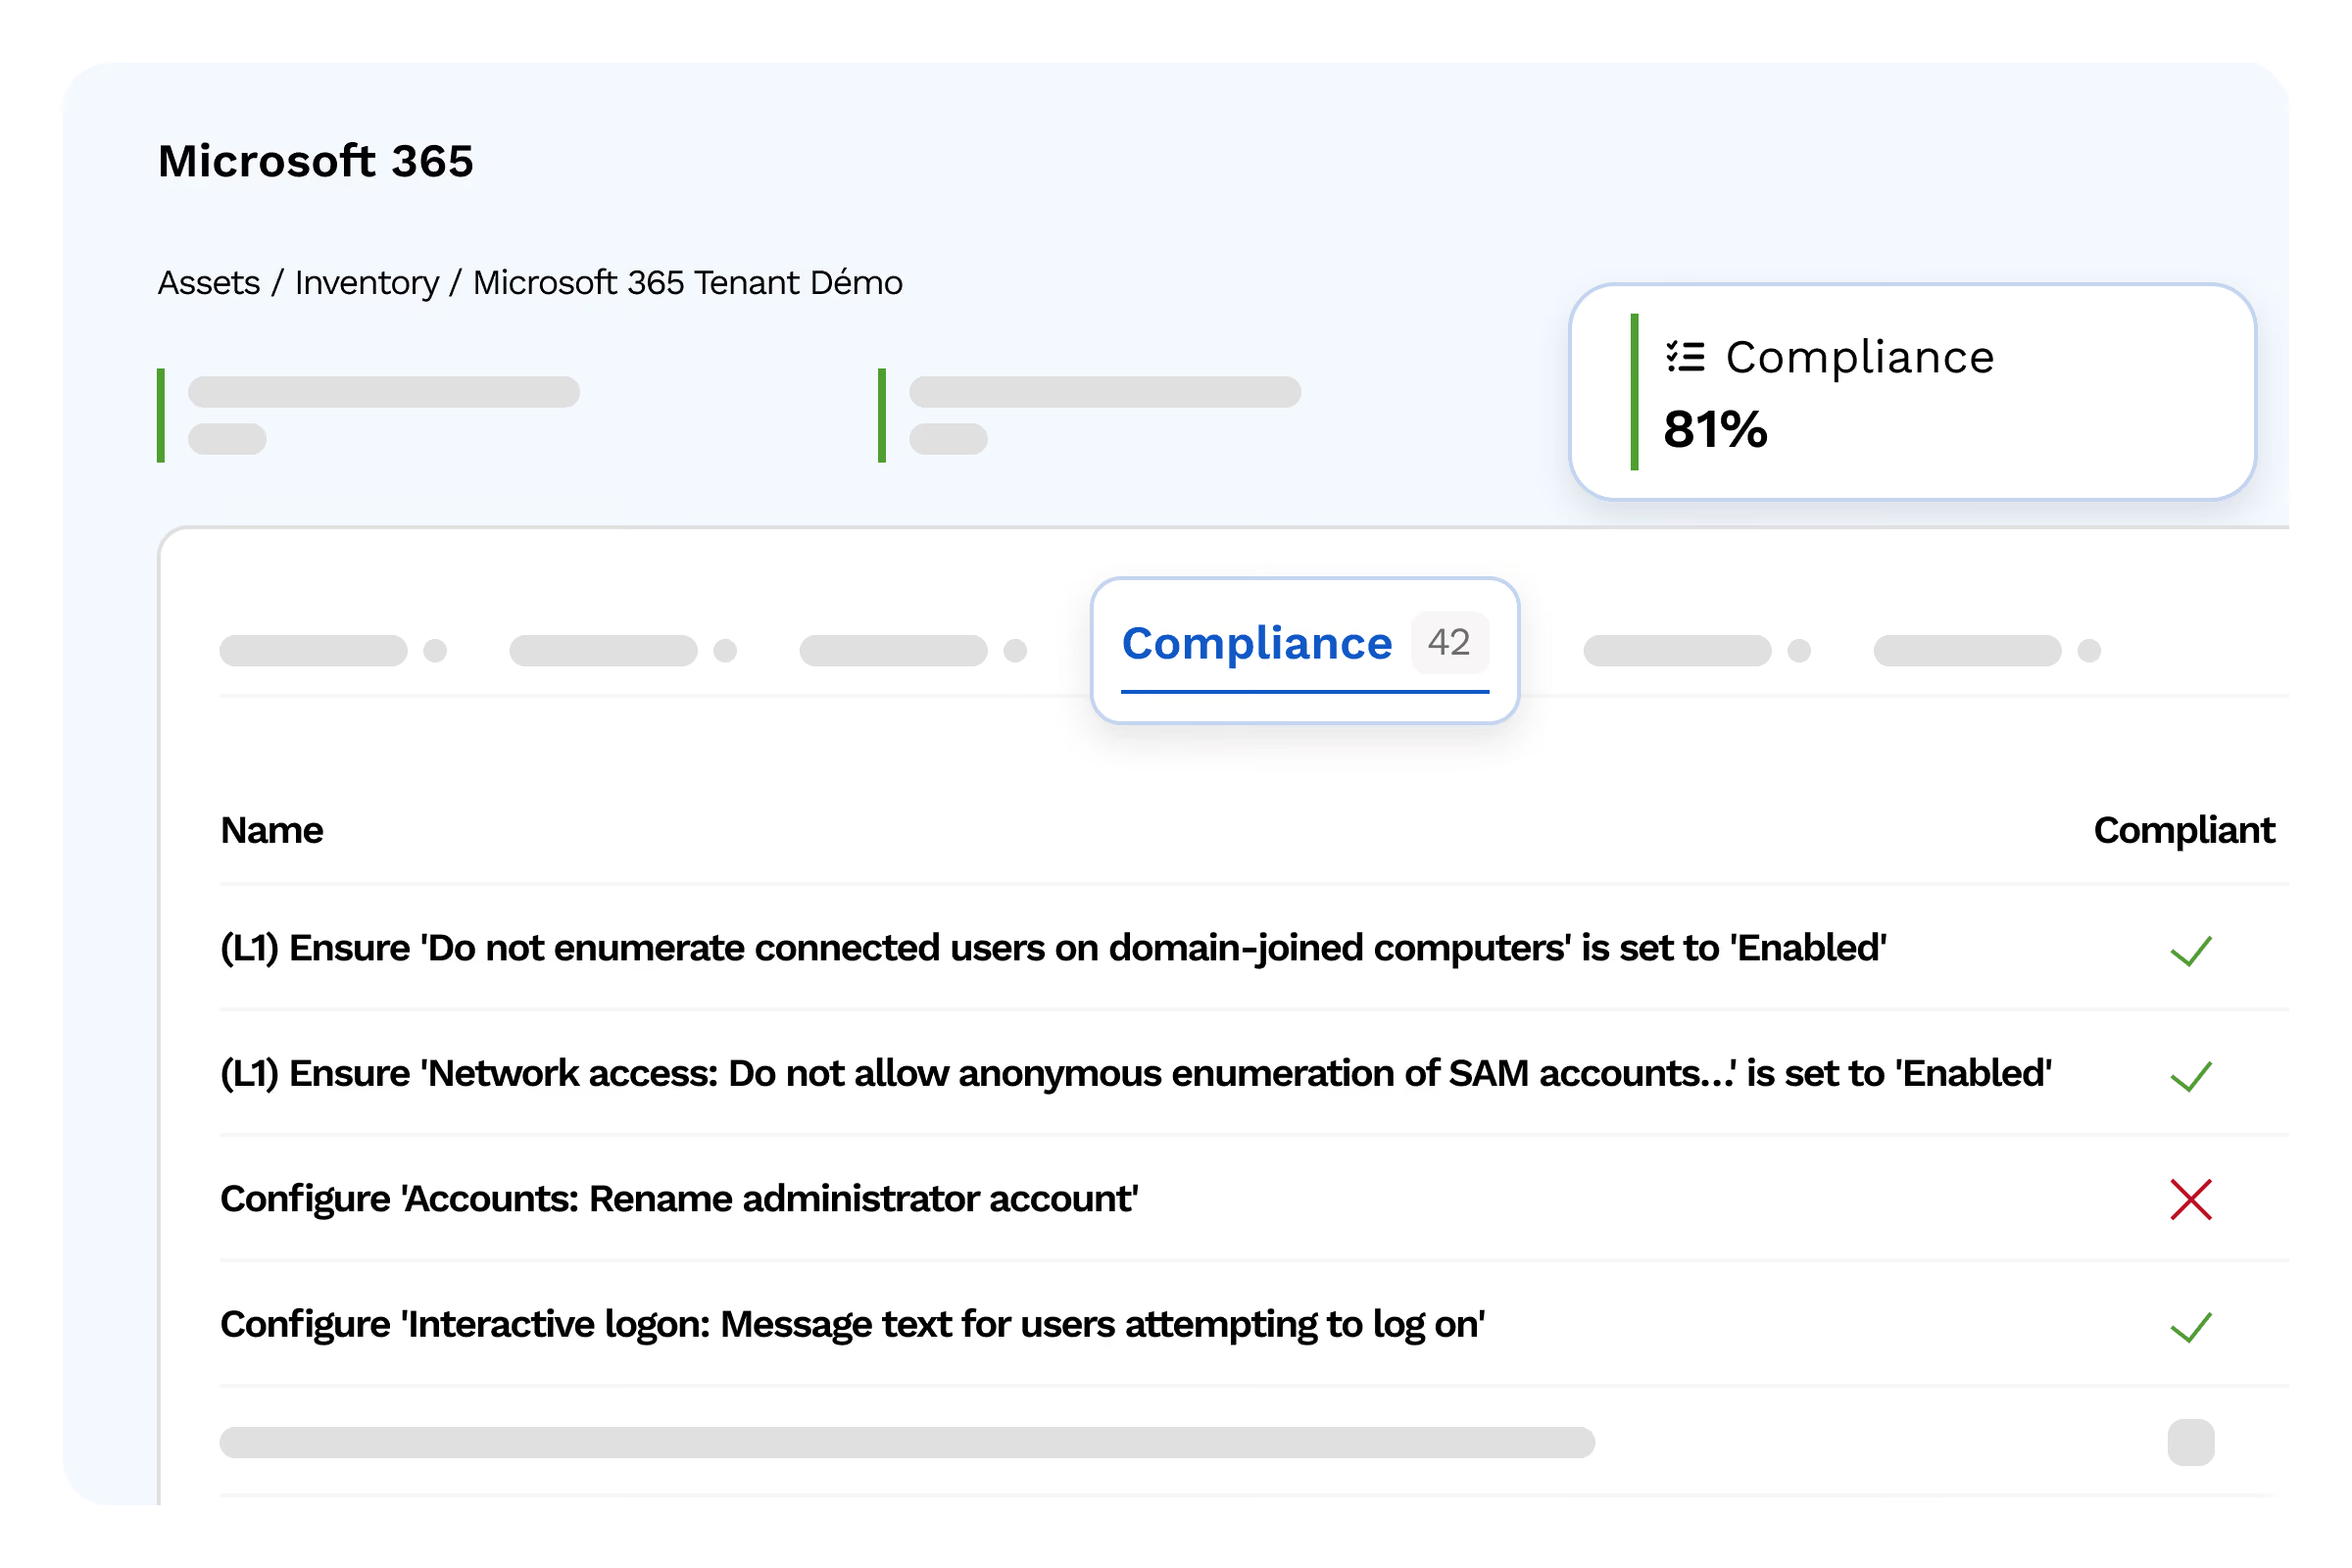
Full visibility into risks associated with your Microsoft identities.
patch management
Patch Management
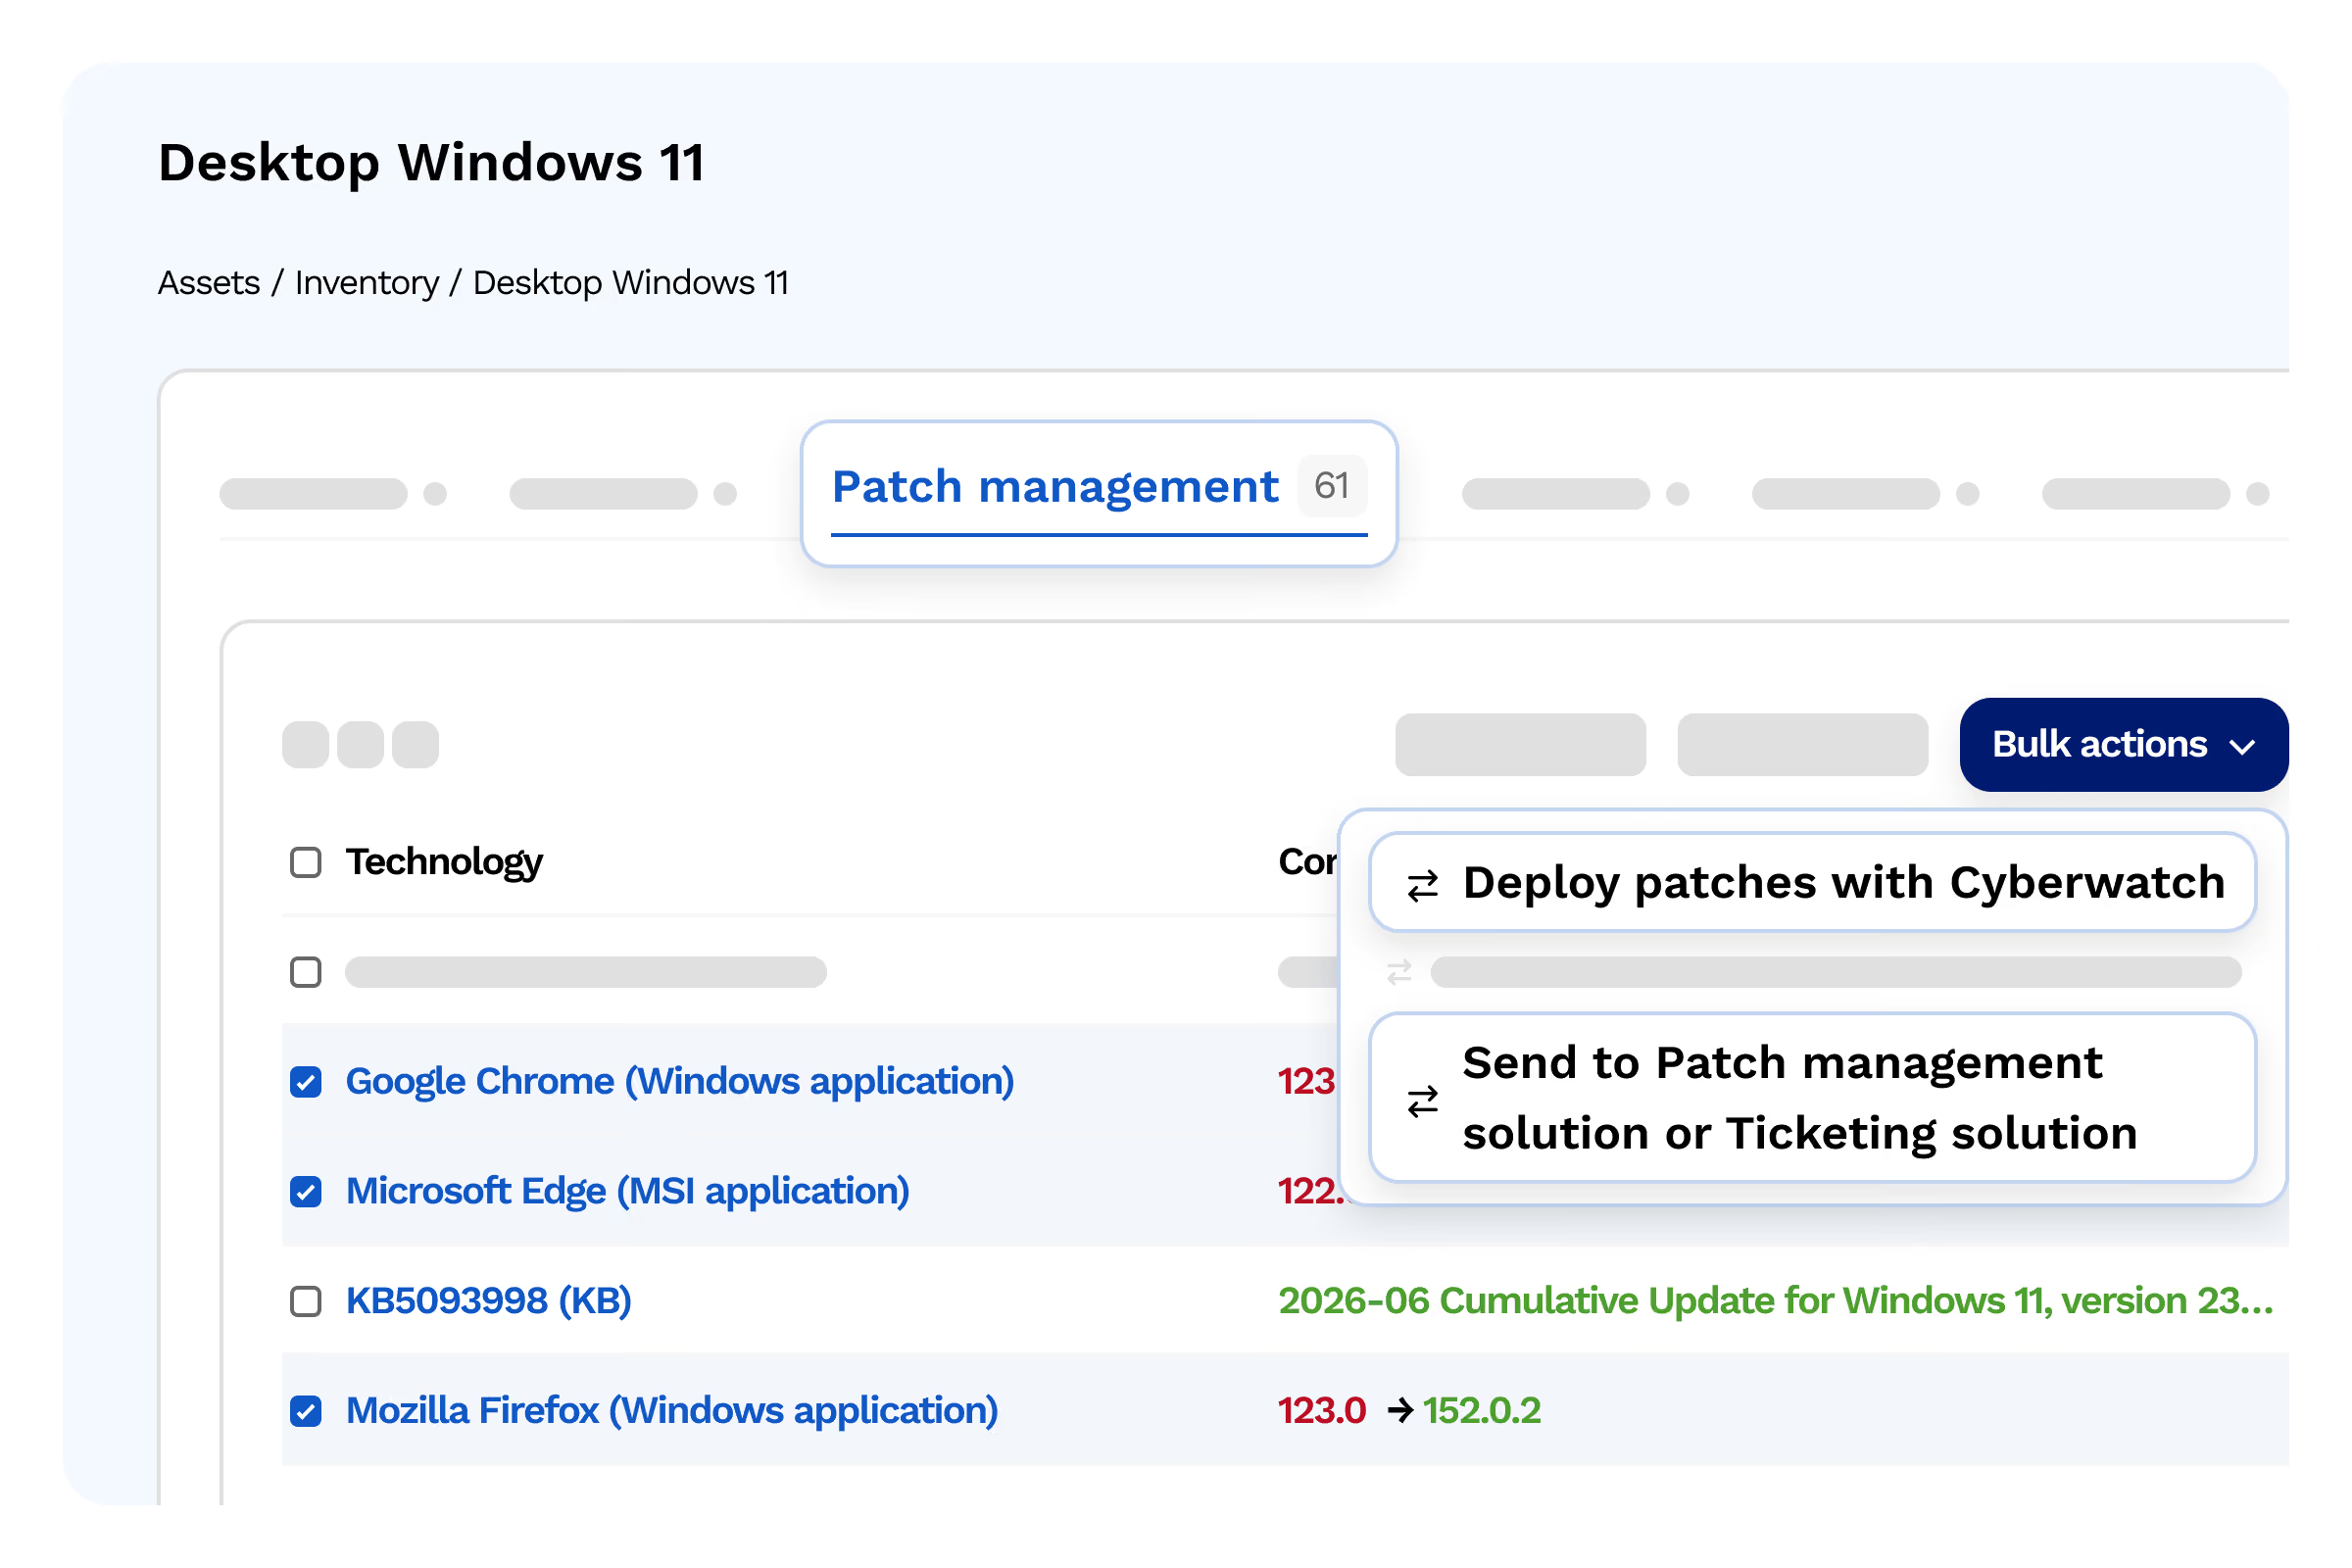
Orchestrate patches natively and integrate your existing tools: ServiceNow, Jira, GLPI, WAPT, Ivanti.
Native Windows + Linux patching
Direct deployment via Windows Update, YUM, and APT with granular scheduling
- Item 1
- Item 2
- Item 3
Patch tool connectors
Bidirectional synchronization with WAPT, CoreUpdate, Ivanti, and more
- Item 1
- Item 2
- Item 3
ITSM integration
ServiceNow, Jira, and GLPI connectors for change traceability and approvals
- Item 1
- Item 2
- Item 3
Business context adaptation
Windows Patch Tuesday, business calendars, and freeze periods during sensitive times
- Item 1
- Item 2
- Item 3
From detection to deployment, without switching tools.
Testimonials
FAQ
From asset mapping to automated remediation.
What is an agent-based or agentless vulnerability scanner?
An agent-based vulnerability scanner installs lightweight software on every server, application, or workstation to be scanned, even when offline. An agentless scanner queries machines remotely without requiring any installation. Cyberwatch Endpoint offers both modes to adapt to your heterogeneous environment and operational constraints.
How does patch management work at Cyberwatch?
Patch management natively orchestrates the deployment of patches identified by the vulnerability scanner, without disrupting your processes. Cyberwatch also integrates with your existing tools (ServiceNow, Jira, GLPI, WAPT, Ivanti) to automate the entire cycle, from vulnerability detection to deployment validation, reducing exposure time.
What are CIS Benchmarks and why should you check them?
CIS Benchmarks are recognized secure configuration standards covering operating systems, databases, and middleware. Cyberwatch continuously assesses your servers, workstations, and VMs for compliance with these hardening standards to detect misconfigurations, which are often just as critical an entry point as an unpatched software vulnerability.
Can Cyberwatch Endpoint audit Microsoft 365 and Entra ID?
Yes, Cyberwatch audits identities, permissions, and data sharing within your Microsoft 365 and Entra ID ecosystem. This comprehensive visibility into identity-related risks complements the technical analysis of servers and workstations, covering both software vulnerabilities and cloud access or configuration weaknesses.
Does Cyberwatch Endpoint also cover the cloud and the external surface?
Cyberwatch Endpoint focuses on servers, workstations, and VMs, but integrates natively with the other modules of the Cyberwatch platform: CSPM and container security for the cloud, EASM and DAST for the external surface, and SCA and SBOM for DevSecOps. A single platform thus centralizes your entire cyber exposure.