
Vulnerability management for industrial environments (OT/ICS/SCADA)
Vulnerability scanner for OT/ICS/SCADA environments. Automatic inventory of industrial PLCs (Rockwell, Schneider, Siemens), native SNMP connectors, air-gap mode, and non-intrusive monitoring. Cyberwatch secures your industrial networks without impacting your production processes.
Asset inventory: the major challenge for OT security
Industrial environments are home to heterogeneous equipment that is often aging, rarely documented, and increasingly connected. Shadow IT/OT—assets that are uninventoried, forgotten, or added without validation—is the primary risk factor. Without an exhaustive and up-to-date inventory, it is impossible to know what is vulnerable, what is exposed, or what needs to be prioritized for remediation.

Shadow IT / OT

Unlisted equipment connected to the network without oversight creates invisible entry points for attackers.
Outdated manual inventories

Excel files and self-reported inventories never reflect the reality on the ground. Gaps widen with every maintenance intervention.
Strict regulations

NIS2 and LPM regulations require an up-to-date inventory of critical industrial assets, complete with traceability and audit trails.
Inventory
Automatic discovery of your industrial assets
Eliminate shadow OT with automatic, non-intrusive mapping
automatically discovers your industrial assets using two complementary methods, without disrupting your production processes.
Safe Query — direct and secure interrogation:
Native Windows + Linux patching
Non-disruptive device polling via appropriate protocols
- Item 1
- Item 2
- Item 3
Patch management connectors
Zero impact on production: no writing, no modification of PLC settings
- Item 1
- Item 2
- Item 3
Native Windows + Linux patching
Automatic retrieval of inventory information: model, firmware, version, status
- Item 1
- Item 2
- Item 3
Native Windows + Linux patching
All methods tested in our OT laboratory to ensure system stability
- Item 1
- Item 2
- Item 3
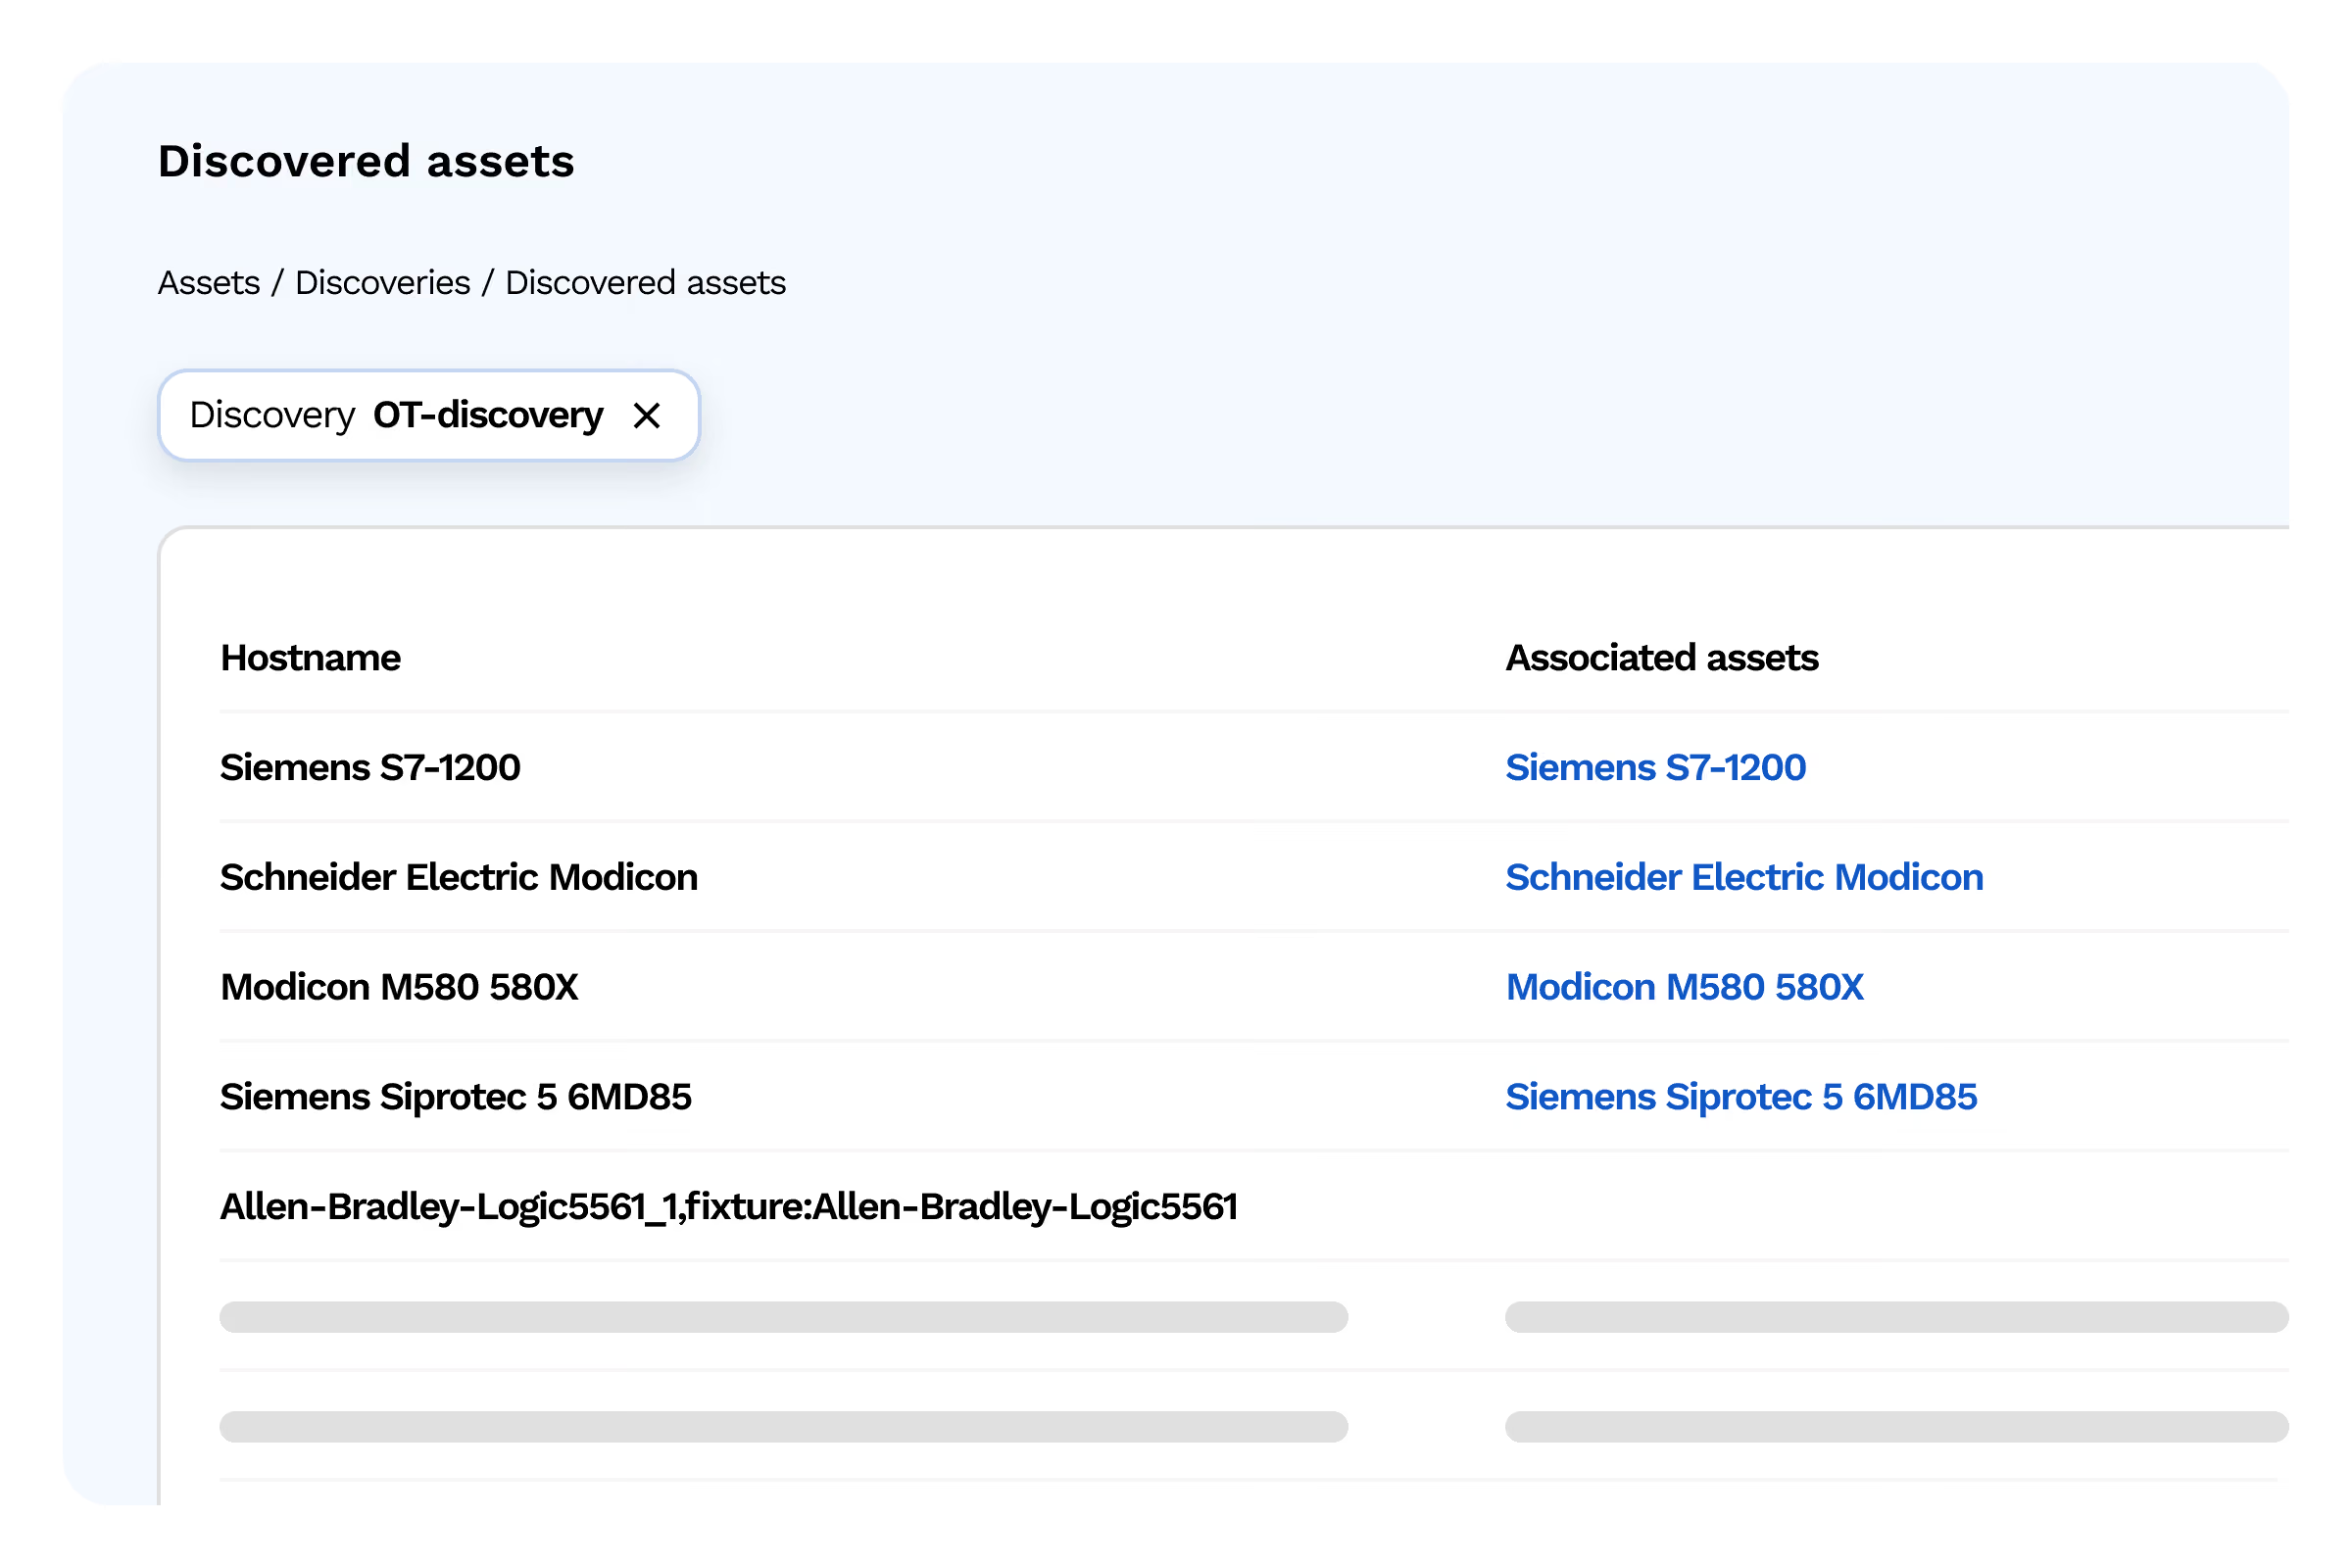
Interconnection with OT network sensors:
Nozomi Networks
Inventory import from Nozomi probes already deployed on your industrial networks
- Item 1
- Item 2
- Item 3
Allentis (a Framatome subsidiary)
Native connector for ANSSI-qualified Allentis NDR probes for unified IT/OT mapping
- Item 1
- Item 2
- Item 3
Seckiot
Integration with Seckiot sensors to enrich OT inventory
- Item 1
- Item 2
- Item 3
Seckiot
Correlation between network data (probes) and system data (Safe Query) for a complete, deduplicated inventory
- Item 1
- Item 2
- Item 3
OT asset discovery is free and unlimited.
Asset coverage
From PLCs to supervision workstations
Comprehensive coverage of your industrial fleet, from PLCs to SCADA servers
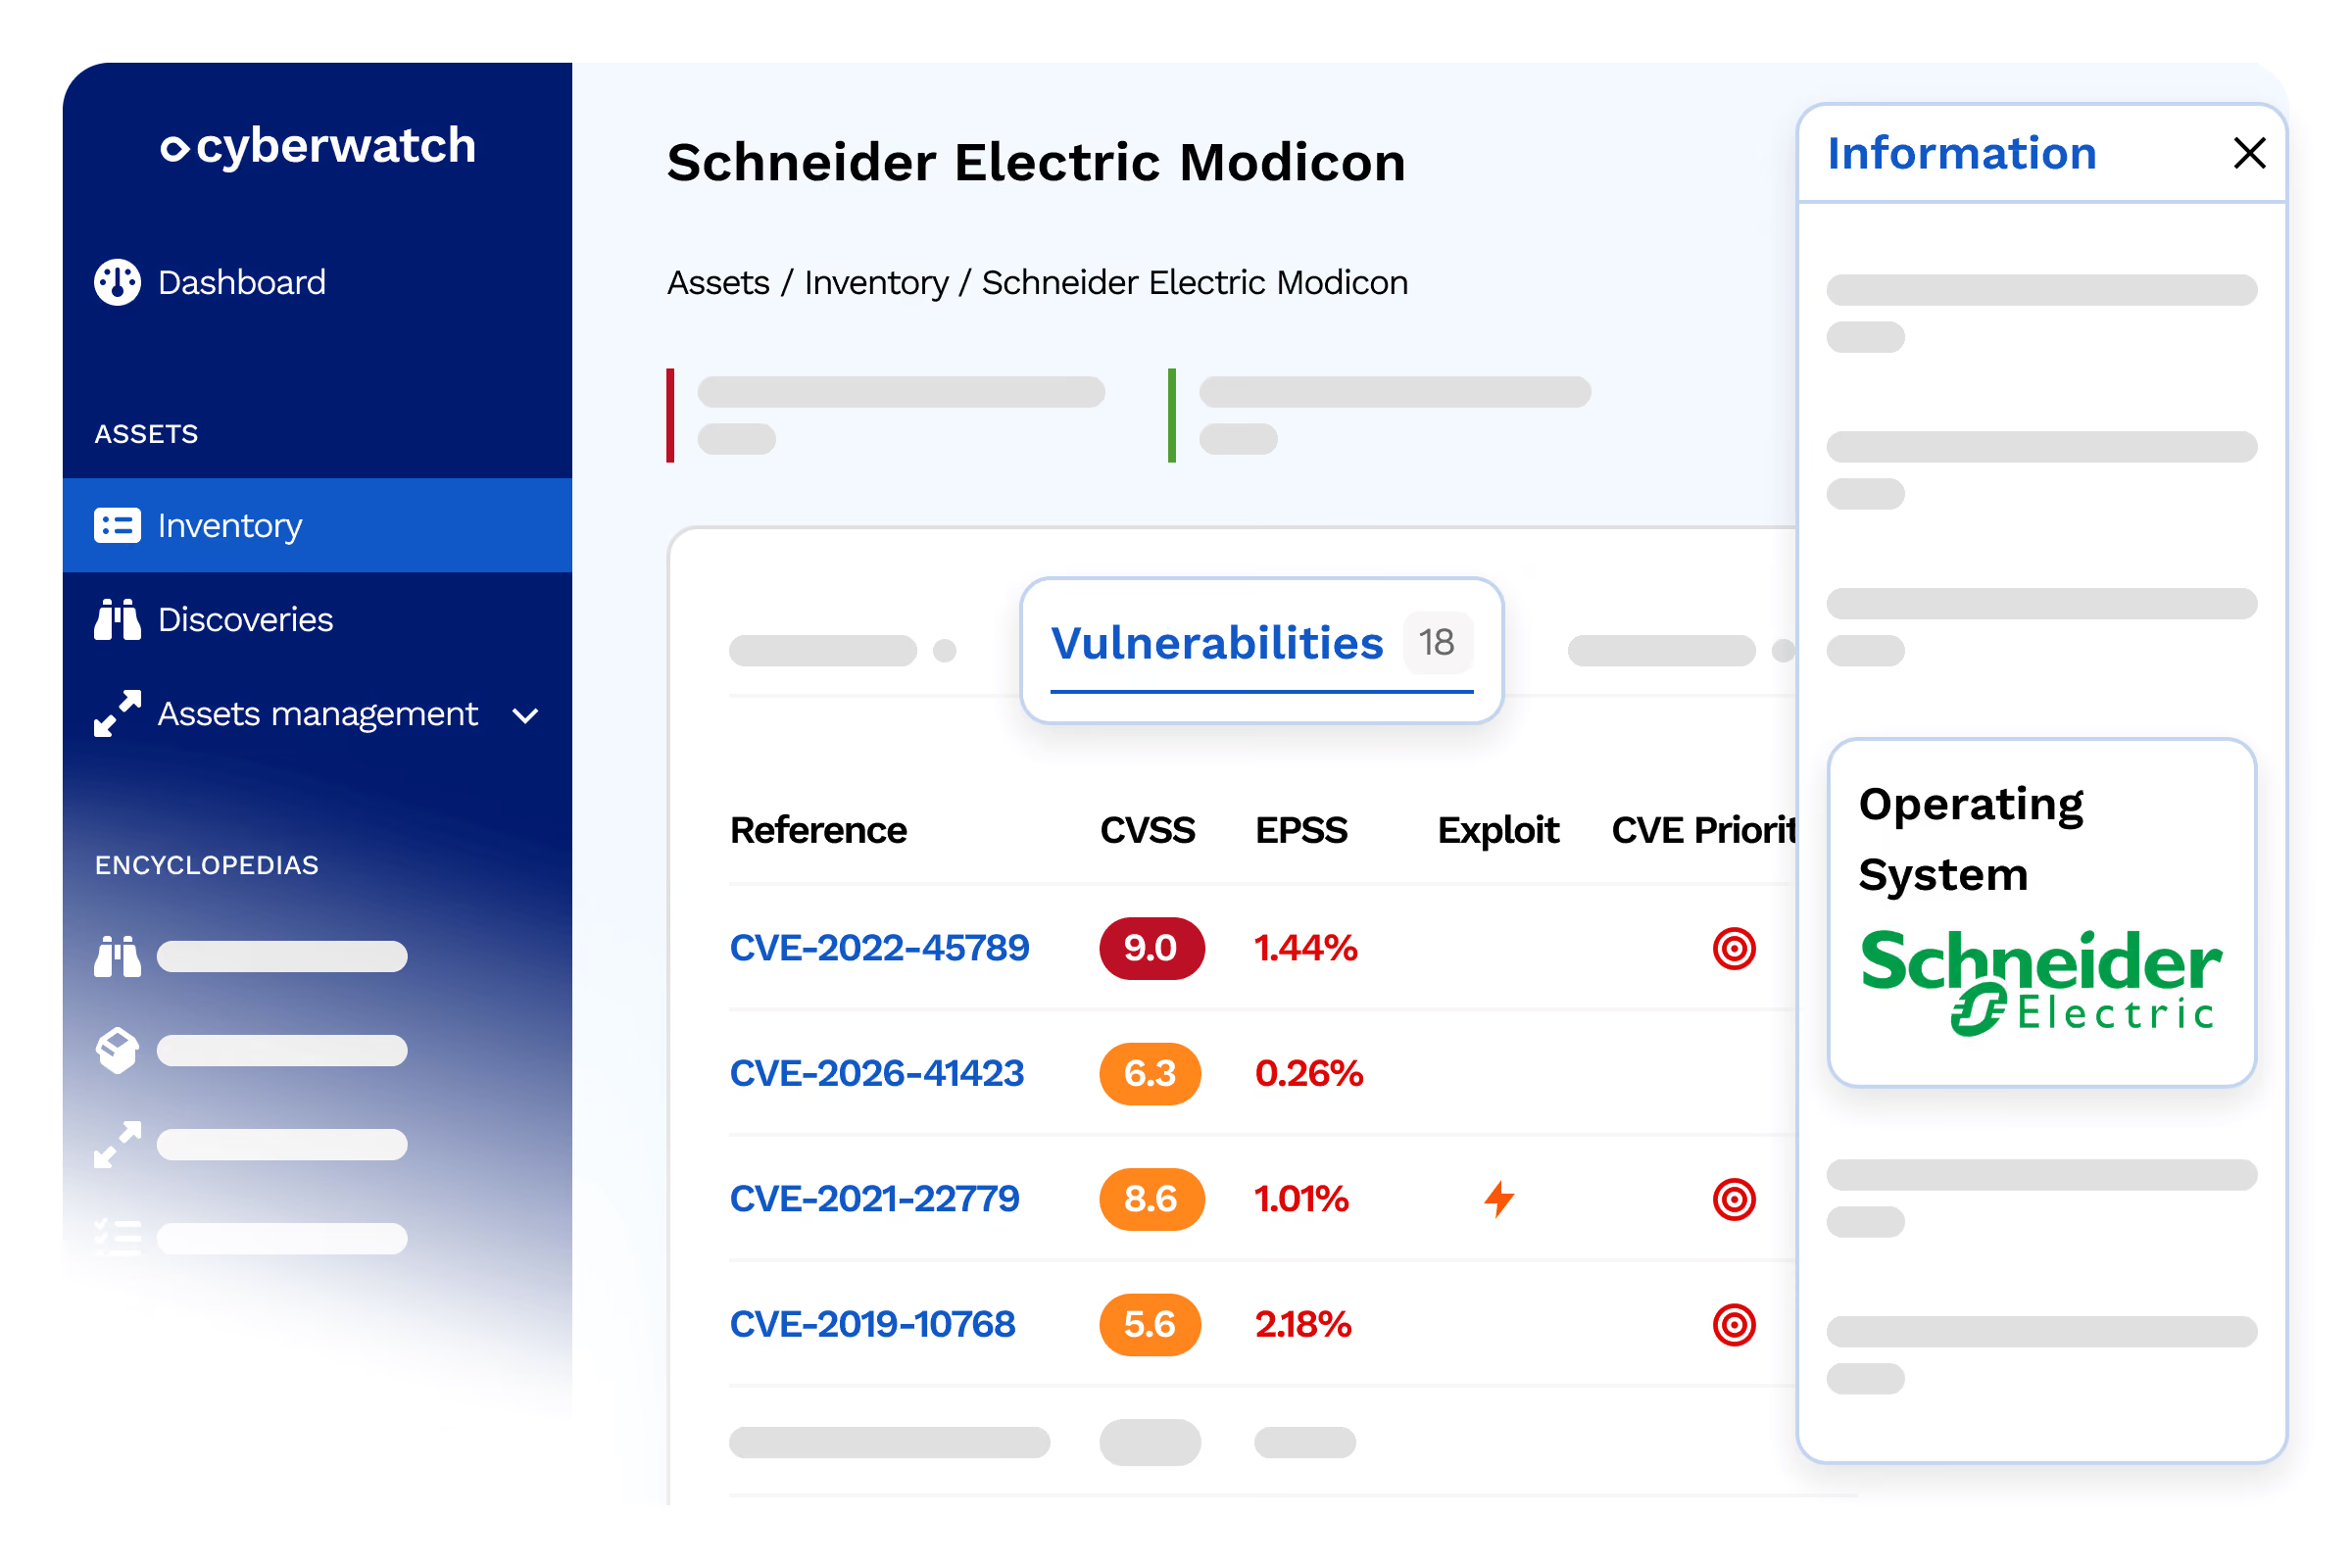
OT networks are not limited to PLCs. Cyberwatch covers the entire chain—industrial equipment, network infrastructure, supervision servers, and operator workstations—for a unified view of your exposure.
Programmable Logic Controllers (PLC / RTU):
Read-only polling of devices via native industrial protocols (Modbus TCP, EtherNet/IP, Siemens S7, SNMP)
- ControlLogix, CompactLogix, MicroLogix (via EtherNet/IP)...
- Modicon M340, M580, Premium, Quantum (via Modbus TCP)...
- SIMATIC S7-300, S7-400, S7-1200, S7-1500 (via S7 protocol)...
Industrial network equipment:
Read-only polling of devices via native industrial protocols (Modbus TCP, EtherNet/IP, Siemens S7, SNMP)
- Managed switches, routers, and industrial firewalls (Cisco, Hirschmann, Moxa, Fortinet...)
- SNMP v1/v2c/v3 polling for inventory and firmware vulnerability detection
Servers and workstations:
Read-only querying of equipment via native industrial protocols (Modbus TCP, EtherNet/IP, Siemens S7, SNMP)
- SCADA / DCS servers, HMI supervision stations
- Windows and Linux operator workstations located in industrial networks
- OS and application vulnerability scanning with or without an agent, including on legacy Windows systems (Server 2008, 2012)
Nozomi Networks
Inventory import from Nozomi sensors already deployed on your industrial networks
- Item 1
- Item 2
- Item 3
Allentis (a Framatome subsidiary)
Native connector with Allentis NDR sensors, ANSSI-qualified, for unified IT/OT mapping
- Item 1
- Item 2
- Item 3
Seckiot
Integration with Seckiot probes to enrich the OT inventory
- Item 1
- Item 2
- Item 3
Seckiot
Correlation between network data (probes) and system data (Safe Query) for a complete and deduplicated inventory
- Item 1
- Item 2
- Item 3
Non-intrusive monitoring
Scan your isolated systems without connecting them to the network
Some critical systems cannot be connected to a scanner. Cyberwatch adapts.
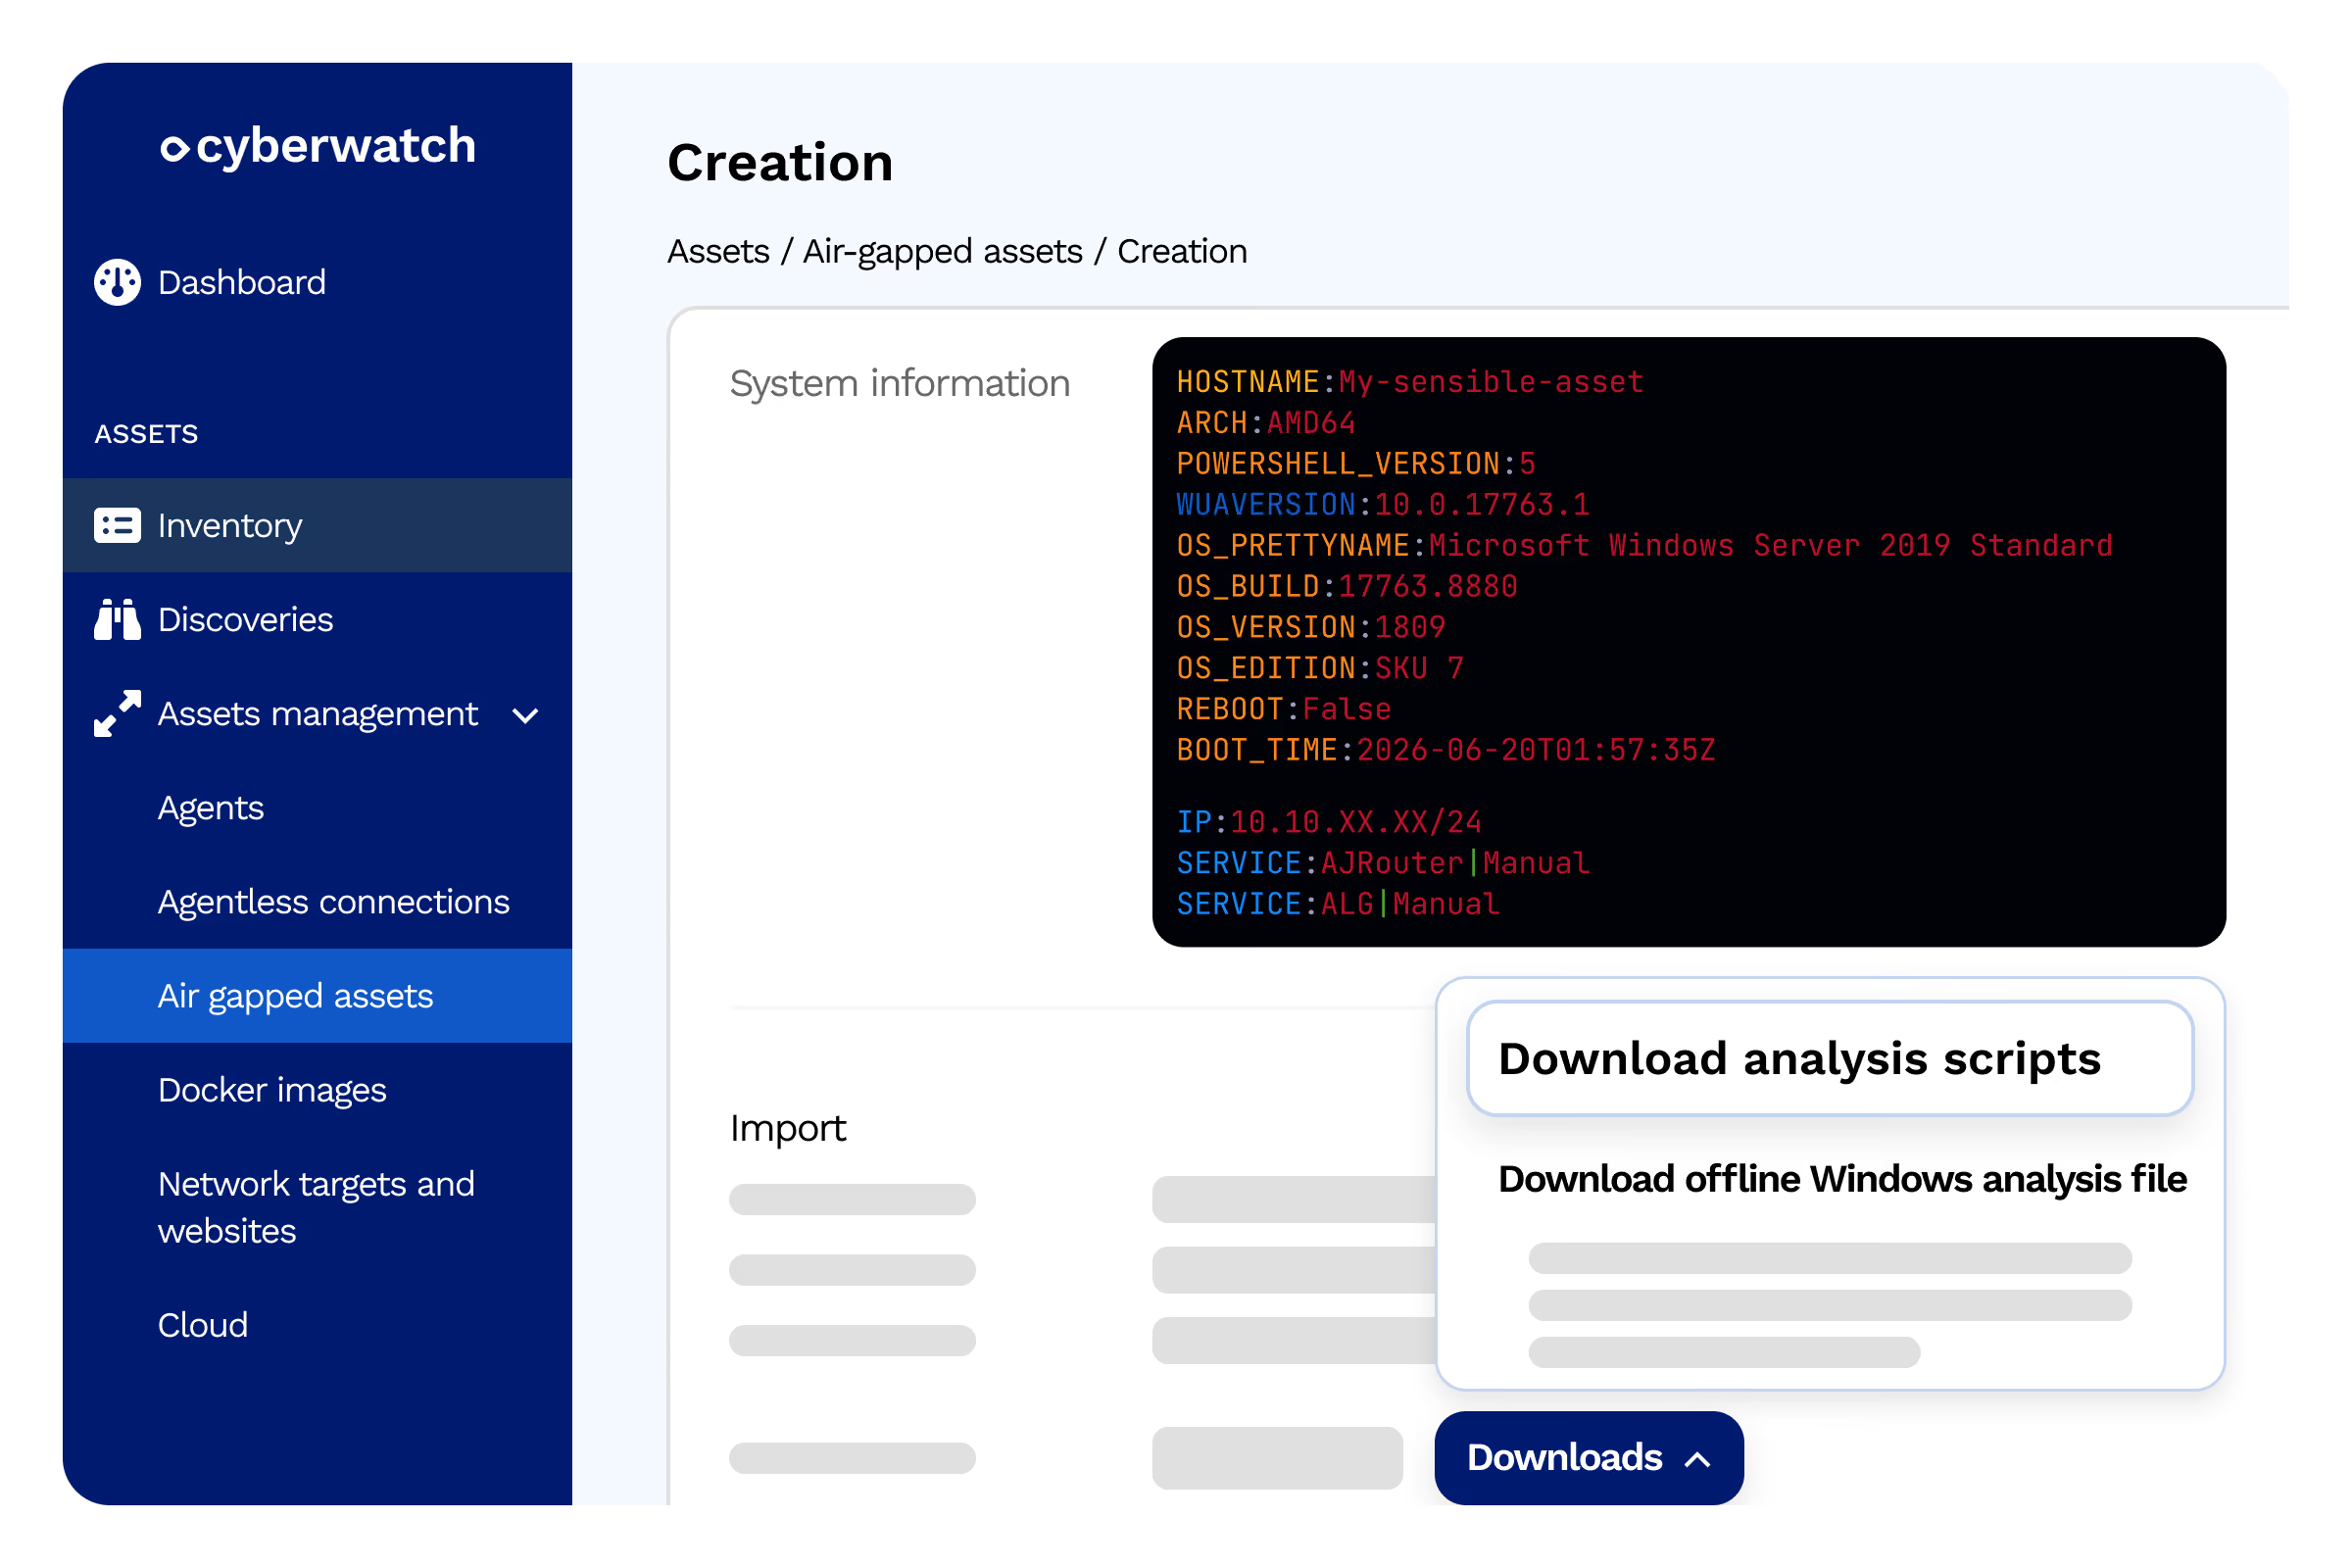
In the most sensitive environments (production plants, safety systems, air-gapped networks), it is sometimes impossible to connect equipment to the Cyberwatch platform. For these cases, Cyberwatch offers a non-intrusive monitoring mode using remote scripts.
CIS Benchmarks
Deployment of lightweight scripts (PowerShell, Bash) directly on isolated systems
- Item 1
- Item 2
- Item 3
CIS Benchmarks
Scripts collect system inventory: OS, installed packages, firmware versions, and configurations
- Item 1
- Item 2
- Item 3
CIS Benchmarks
Results exported as text files, transferable via USB drive or any other removable media
- Item 1
- Item 2
- Item 3
CIS Benchmarks
Import into the central Cyberwatch console for vulnerability and compliance analysis
- Item 1
- Item 2
- Item 3
CIS Benchmarks
Update existing assets or automatically create new ones with each import
- Item 1
- Item 2
- Item 3
Zero network connection required — inventory is transferred via removable media (USB drive).
Air-gap
A complete Cyberwatch console, totally isolated from the Internet
Install Cyberwatch in a network that never communicates with the outside world
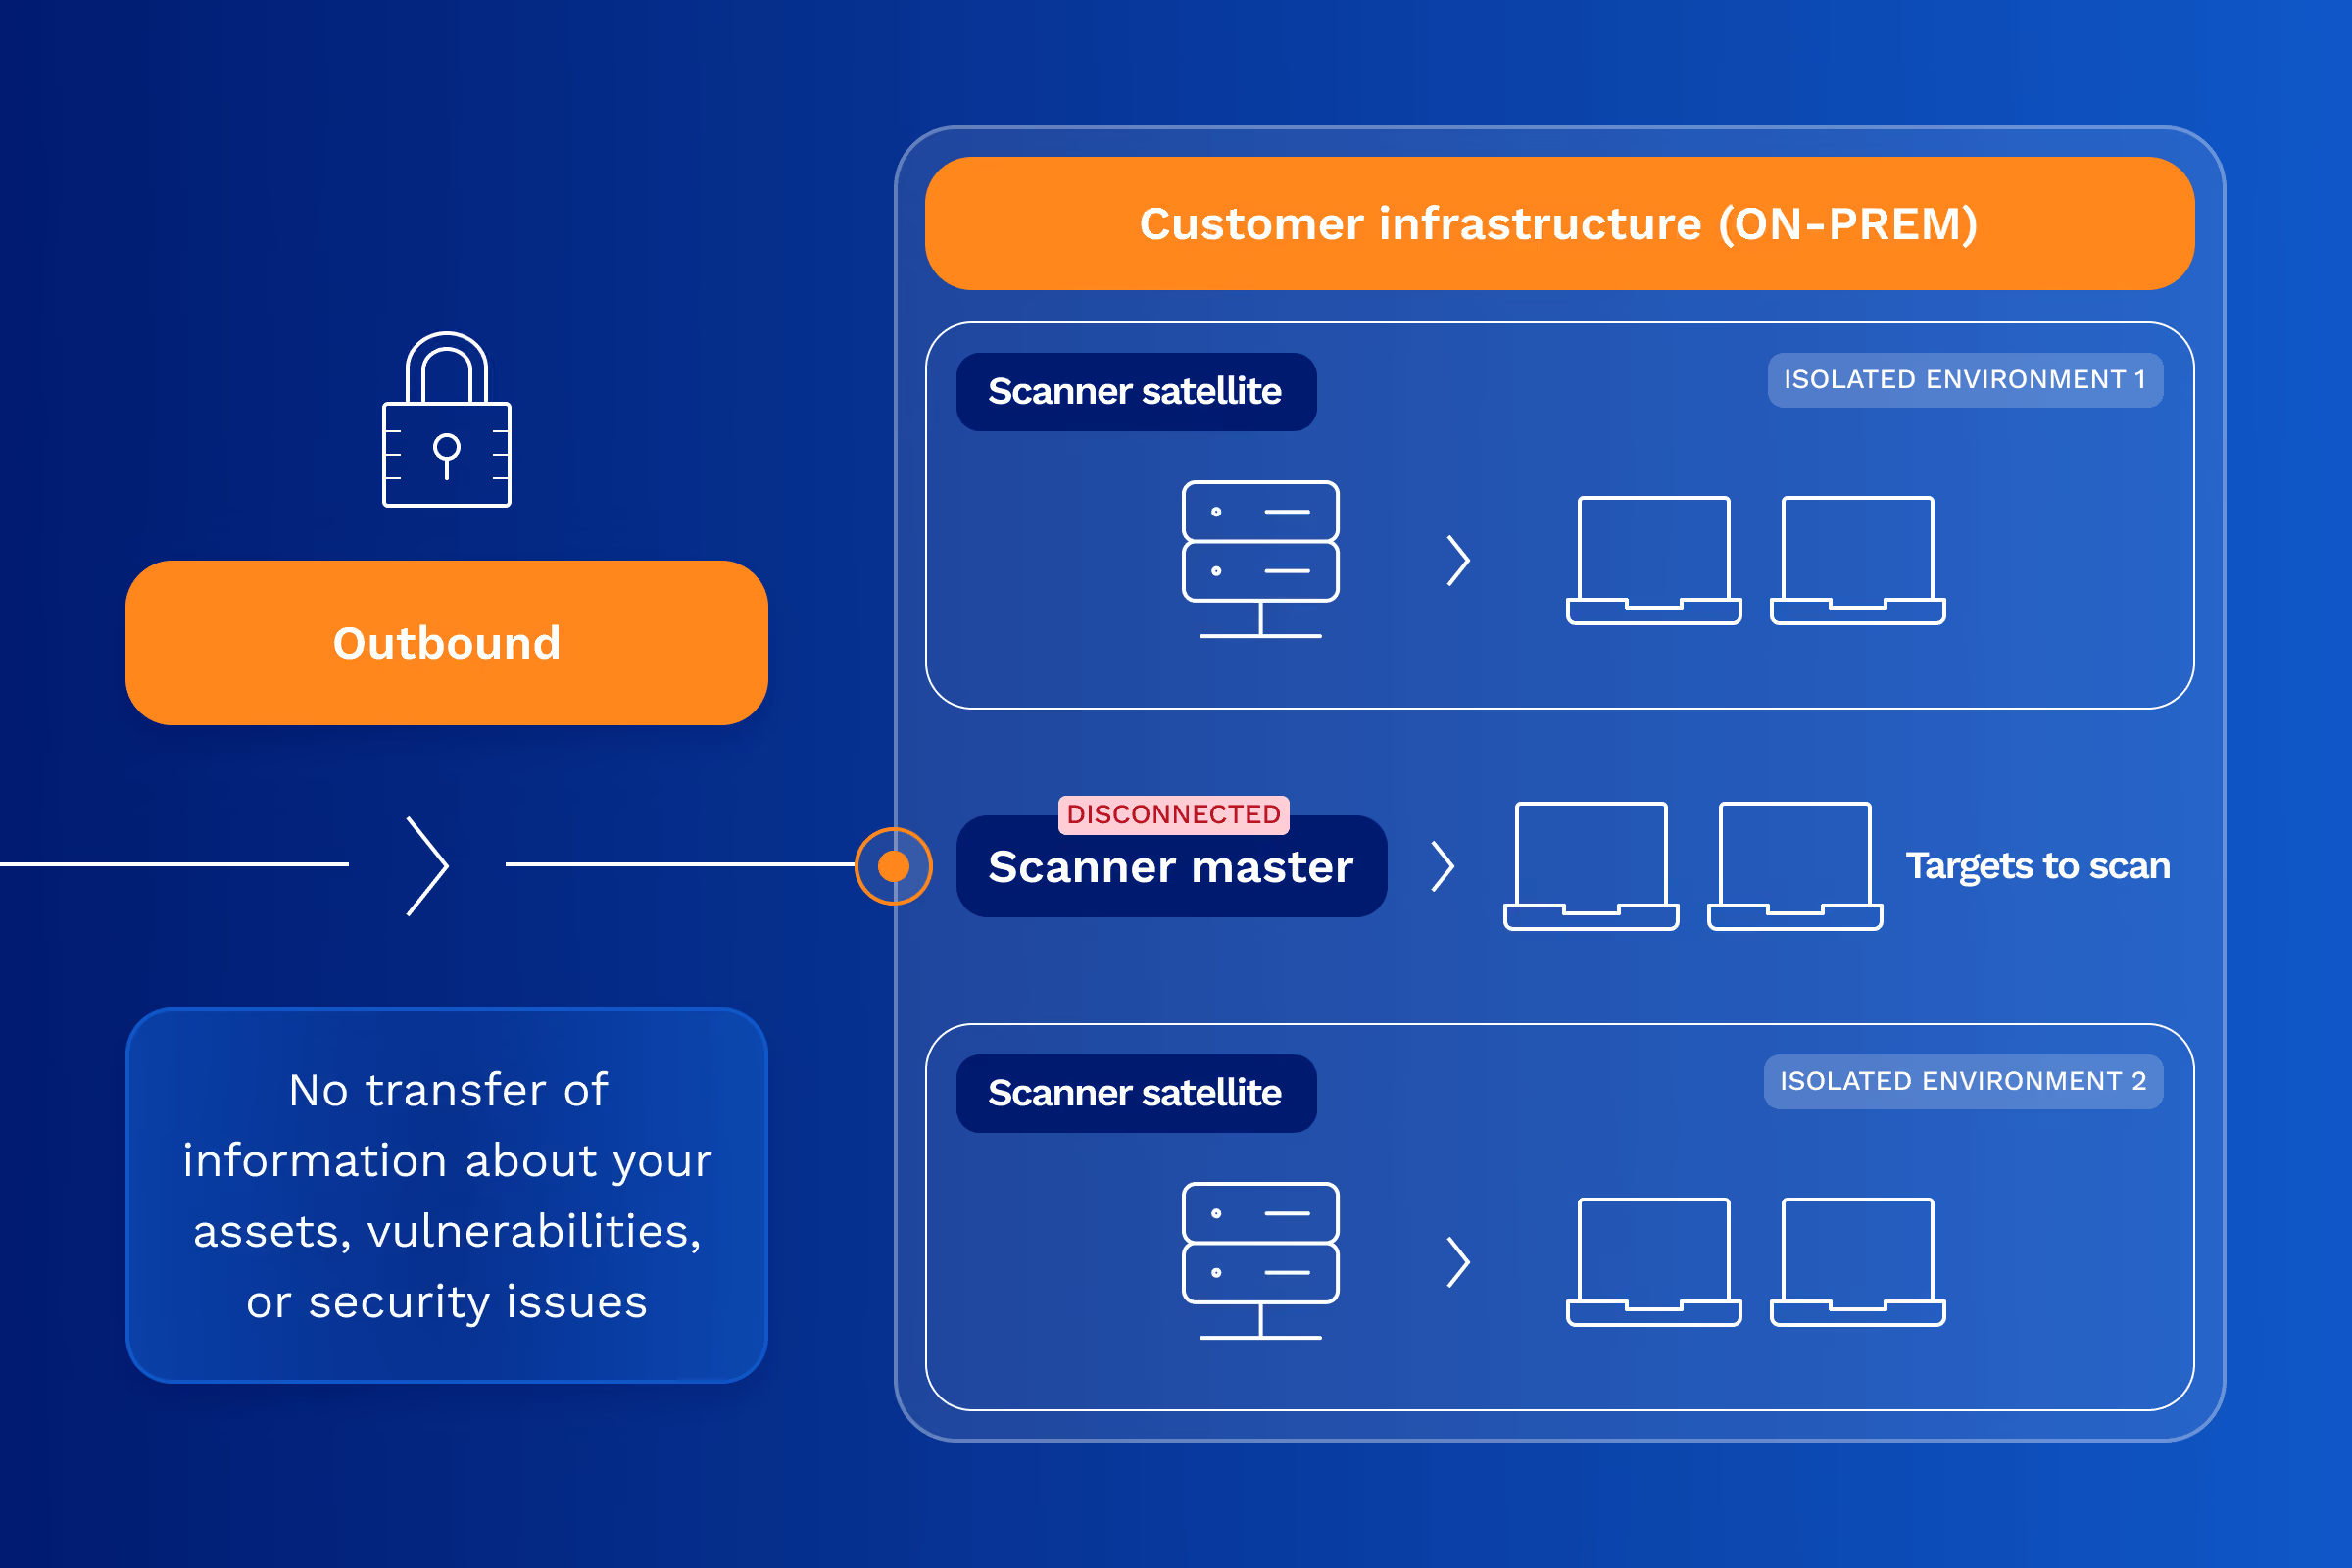
For environments subject to the strictest network isolation requirements, Cyberwatch offers a full air-gap mode. A Cyberwatch console is installed inside the isolated network with no outbound connections. The vulnerability database is updated via manual import.
Programmable Logic Controllers (PLC / RTU):
Installation of a full-featured Cyberwatch console within the isolated network
- Rockwell Automation— ControlLogix, CompactLogix, MicroLogix (via EtherNet/IP)
- Schneider Electric— Modicon M340, M580, Premium, Quantum (via Modbus TCP)
- Siemens— SIMATIC S7-300, S7-400, S7-1200, S7-1500 (via S7 protocol)
Programmable Logic Controllers (PLC / RTU):
No Internet communication: the console never contacts an external server
- Rockwell Automation— ControlLogix, CompactLogix, MicroLogix (via EtherNet/IP)
- Schneider Electric— Modicon M340, M580, Premium, Quantum (via Modbus TCP)
- Siemens— SIMATIC S7-300, S7-400, S7-1200, S7-1500 (via S7 protocol)
Programmable Logic Controllers (PLC / RTU):
Vulnerability database updates (CVE encyclopedia, scores, exploits) via USB file import
- Rockwell Automation— ControlLogix, CompactLogix, MicroLogix (via EtherNet/IP)
- Schneider Electric— Modicon M340, M580, Premium, Quantum (via Modbus TCP)
- Siemens— SIMATIC S7-300, S7-400, S7-1200, S7-1500 (via S7 protocol)
Programmable Logic Controllers (PLC / RTU):
Vulnerability and compliance scans performed locally, with results viewable directly on the console
- Rockwell Automation— ControlLogix, CompactLogix, MicroLogix (via EtherNet/IP)
- Schneider Electric— Modicon M340, M580, Premium, Quantum (via Modbus TCP)
- Siemens— SIMATIC S7-300, S7-400, S7-1200, S7-1500 (via S7 protocol)
Programmable Logic Controllers (PLC / RTU):
Dashboards, reports, and exports available locally, with no external dependencies
- Rockwell Automation— ControlLogix, CompactLogix, MicroLogix (via EtherNet/IP)
- Schneider Electric— Modicon M340, M580, Premium, Quantum (via Modbus TCP)
- Siemens— SIMATIC S7-300, S7-400, S7-1200, S7-1500 (via S7 protocol)
Nozomi Networks
Inventory import from Nozomi probes already deployed on your industrial networks
- Item 1
- Item 2
- Item 3
Allentis (Framatome subsidiary)
Native connector for Allentis NDR probes, ANSSI-qualified, for unified IT/OT mapping
- Item 1
- Item 2
- Item 3
Seckiot
Integration with Seckiot sensors to enrich the OT inventory
- Item 1
- Item 2
- Item 3
Seckiot
Correlation between network data (probes) and system data (Safe Query) for a complete, deduplicated inventory
- Item 1
- Item 2
- Item 3
Ideal for nuclear sites, defense networks, and critical infrastructure subject to the Military Programming Law (LPM).
Cyberwatch, a subsidiary of Framatome (EDF Group)
OT security is not a theoretical subject for us. Cyberwatch is part of the Framatome group, an EDF subsidiary and world leader in nuclear energy. Securing the most sensitive industrial environments (nuclear power plants, energy production networks, critical infrastructure) is a strategic priority for our group.
This affiliation gives us a unique understanding of the operational, regulatory, and safety constraints that apply to industrial systems. Our solutions are designed and tested to meet the strictest requirements of the nuclear and energy sectors.
Framatome Cybersecurity brings together a comprehensive portfolio of cybersecurity products and services for IT and OT environments, including Cyberwatch (exposure management), Allentis (ANSSI-qualified NDR), and support services dedicated to operators of critical importance.
Testimonials
L'accompagnement de l'équipe Cyberwatch a été déterminant pour déployer la plateforme sur nos sites de production sans perturber nos lignes. Le support dédié répond vite et comprend nos contraintes industrielles.

Exemple à remplacer — DSI, industrie
DSI

Avec Cyberwatch, nous avons enfin une vue exhaustive de notre parc informatique et pouvons prioriser nos actions de remédiation selon un risque réel plutôt qu'une simple liste de CVE. La plateforme s'intègre bien à nos contraintes de souveraineté.
Exemple à remplacer — RSSI, secteur public
RSSI
FAQ
From asset mapping to automated remediation.
How does Cyberwatch discover OT assets?
Cyberwatch combines two non-intrusive methods: Safe Query, a secure, direct interrogation of equipment, and interconnection with existing OT network probes. These approaches respect the constraints specific to industrial environments, where overly aggressive scanning can disrupt a PLC or a critical physical process.
Which regulations require an inventory of industrial assets?
Several regulations require an up-to-date and traceable inventory of critical industrial assets: NIS2 for essential service operators, the LPM (Military Programming Law) for defense infrastructure, and the IEC 62443 standard specific to industrial system cybersecurity. Cyberwatch provides the audit evidence required for these compliance efforts.
Can Cyberwatch monitor systems that are completely isolated from the network (air-gap)?
Yes, for the most sensitive systems (nuclear power plants, safety networks, etc.) that cannot be connected directly, Cyberwatch offers non-intrusive monitoring via remote scripts: the inventory is transferred using removable media without a network connection. A full Cyberwatch console can also be installed in air-gap mode, completely isolated from the Internet, with manual updates for the vulnerability database.
Why trust Cyberwatch to secure sensitive industrial environments?
Cyberwatch is a subsidiary of the Framatome group, which is itself a subsidiary of EDF, a world leader in nuclear energy. This affiliation gives Cyberwatch a direct understanding of the operational, regulatory, and safety constraints specific to the most critical industrial environments (nuclear power plants, energy production infrastructure, etc.), going beyond purely theoretical cybersecurity expertise.