
Air-gapped and sensitive environments
Cyberwatch was designed to meet the highest privacy and security requirements. We offer installation modes ranging from sovereign SaaS to on-premises, and even fully disconnected environments, to match your specific needs and ensure you retain full sovereignty over your data.
Challenges of sensitive environments

Security data confidentiality
Vulnerability scan results are critical information. Exposing them to a third party—whether a software vendor, host, or service provider—is a risk in itself. Data must remain under your exclusive control.

Compliance requirements
Critical infrastructure, defense, nuclear, and essential service providers require segmented architectures, specific clearance levels, and audit trails that standard SaaS solutions cannot provide.

Sovereignty against foreign powers
Extraterritorial regulations (such as the Cloud Act or FISA) allow third-party states to access data hosted by their nationals. Using a French software provider hosted in France eliminates this legal risk.

Air-gapped
Fully air-gapped mode
A complete Cyberwatch console, fully isolated from the Internet
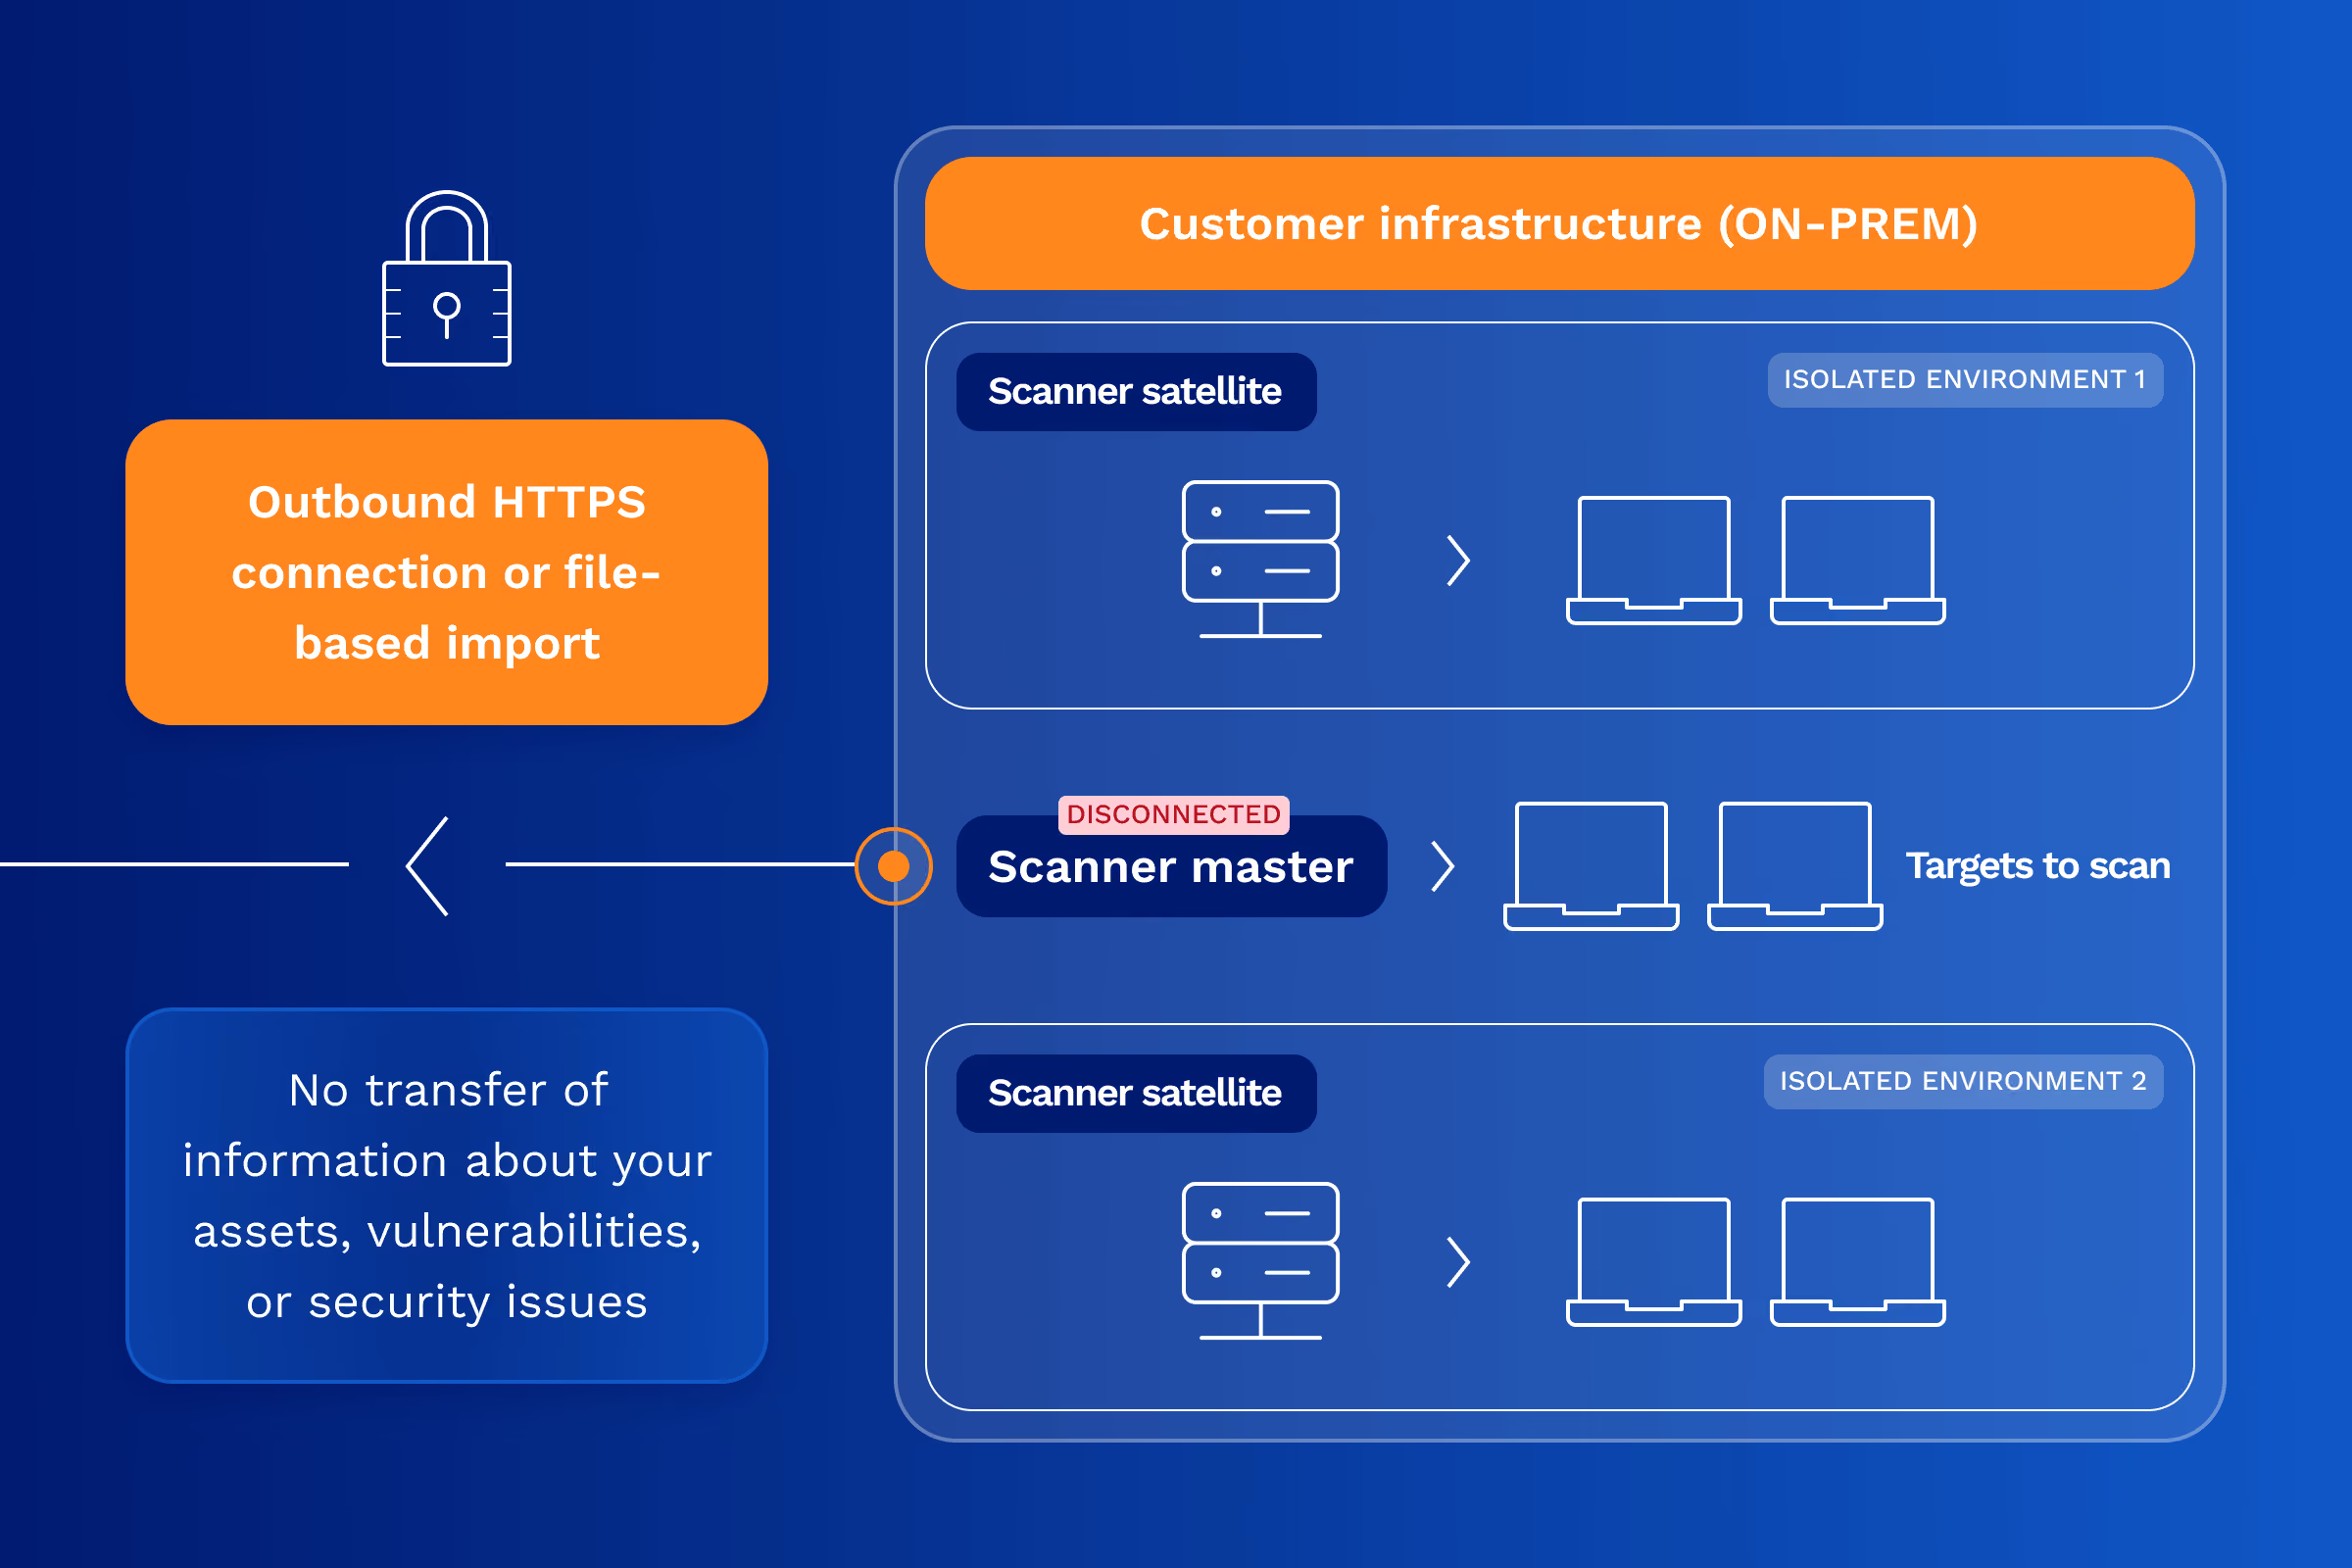
Cyberwatch installs entirely within your disconnected network, with no outgoing connections. The CVE vulnerability database is updated via manual import using secure media. All features are available: scanning, compliance, reporting, and patch management.
Zero Internet connection
No network dependencies, fully autonomous operation
- Item 1
- Item 2
- Item 3
Local CVE database
Update via secure transfer on removable media, with no exposure
- Item 1
- Item 2
- Item 3
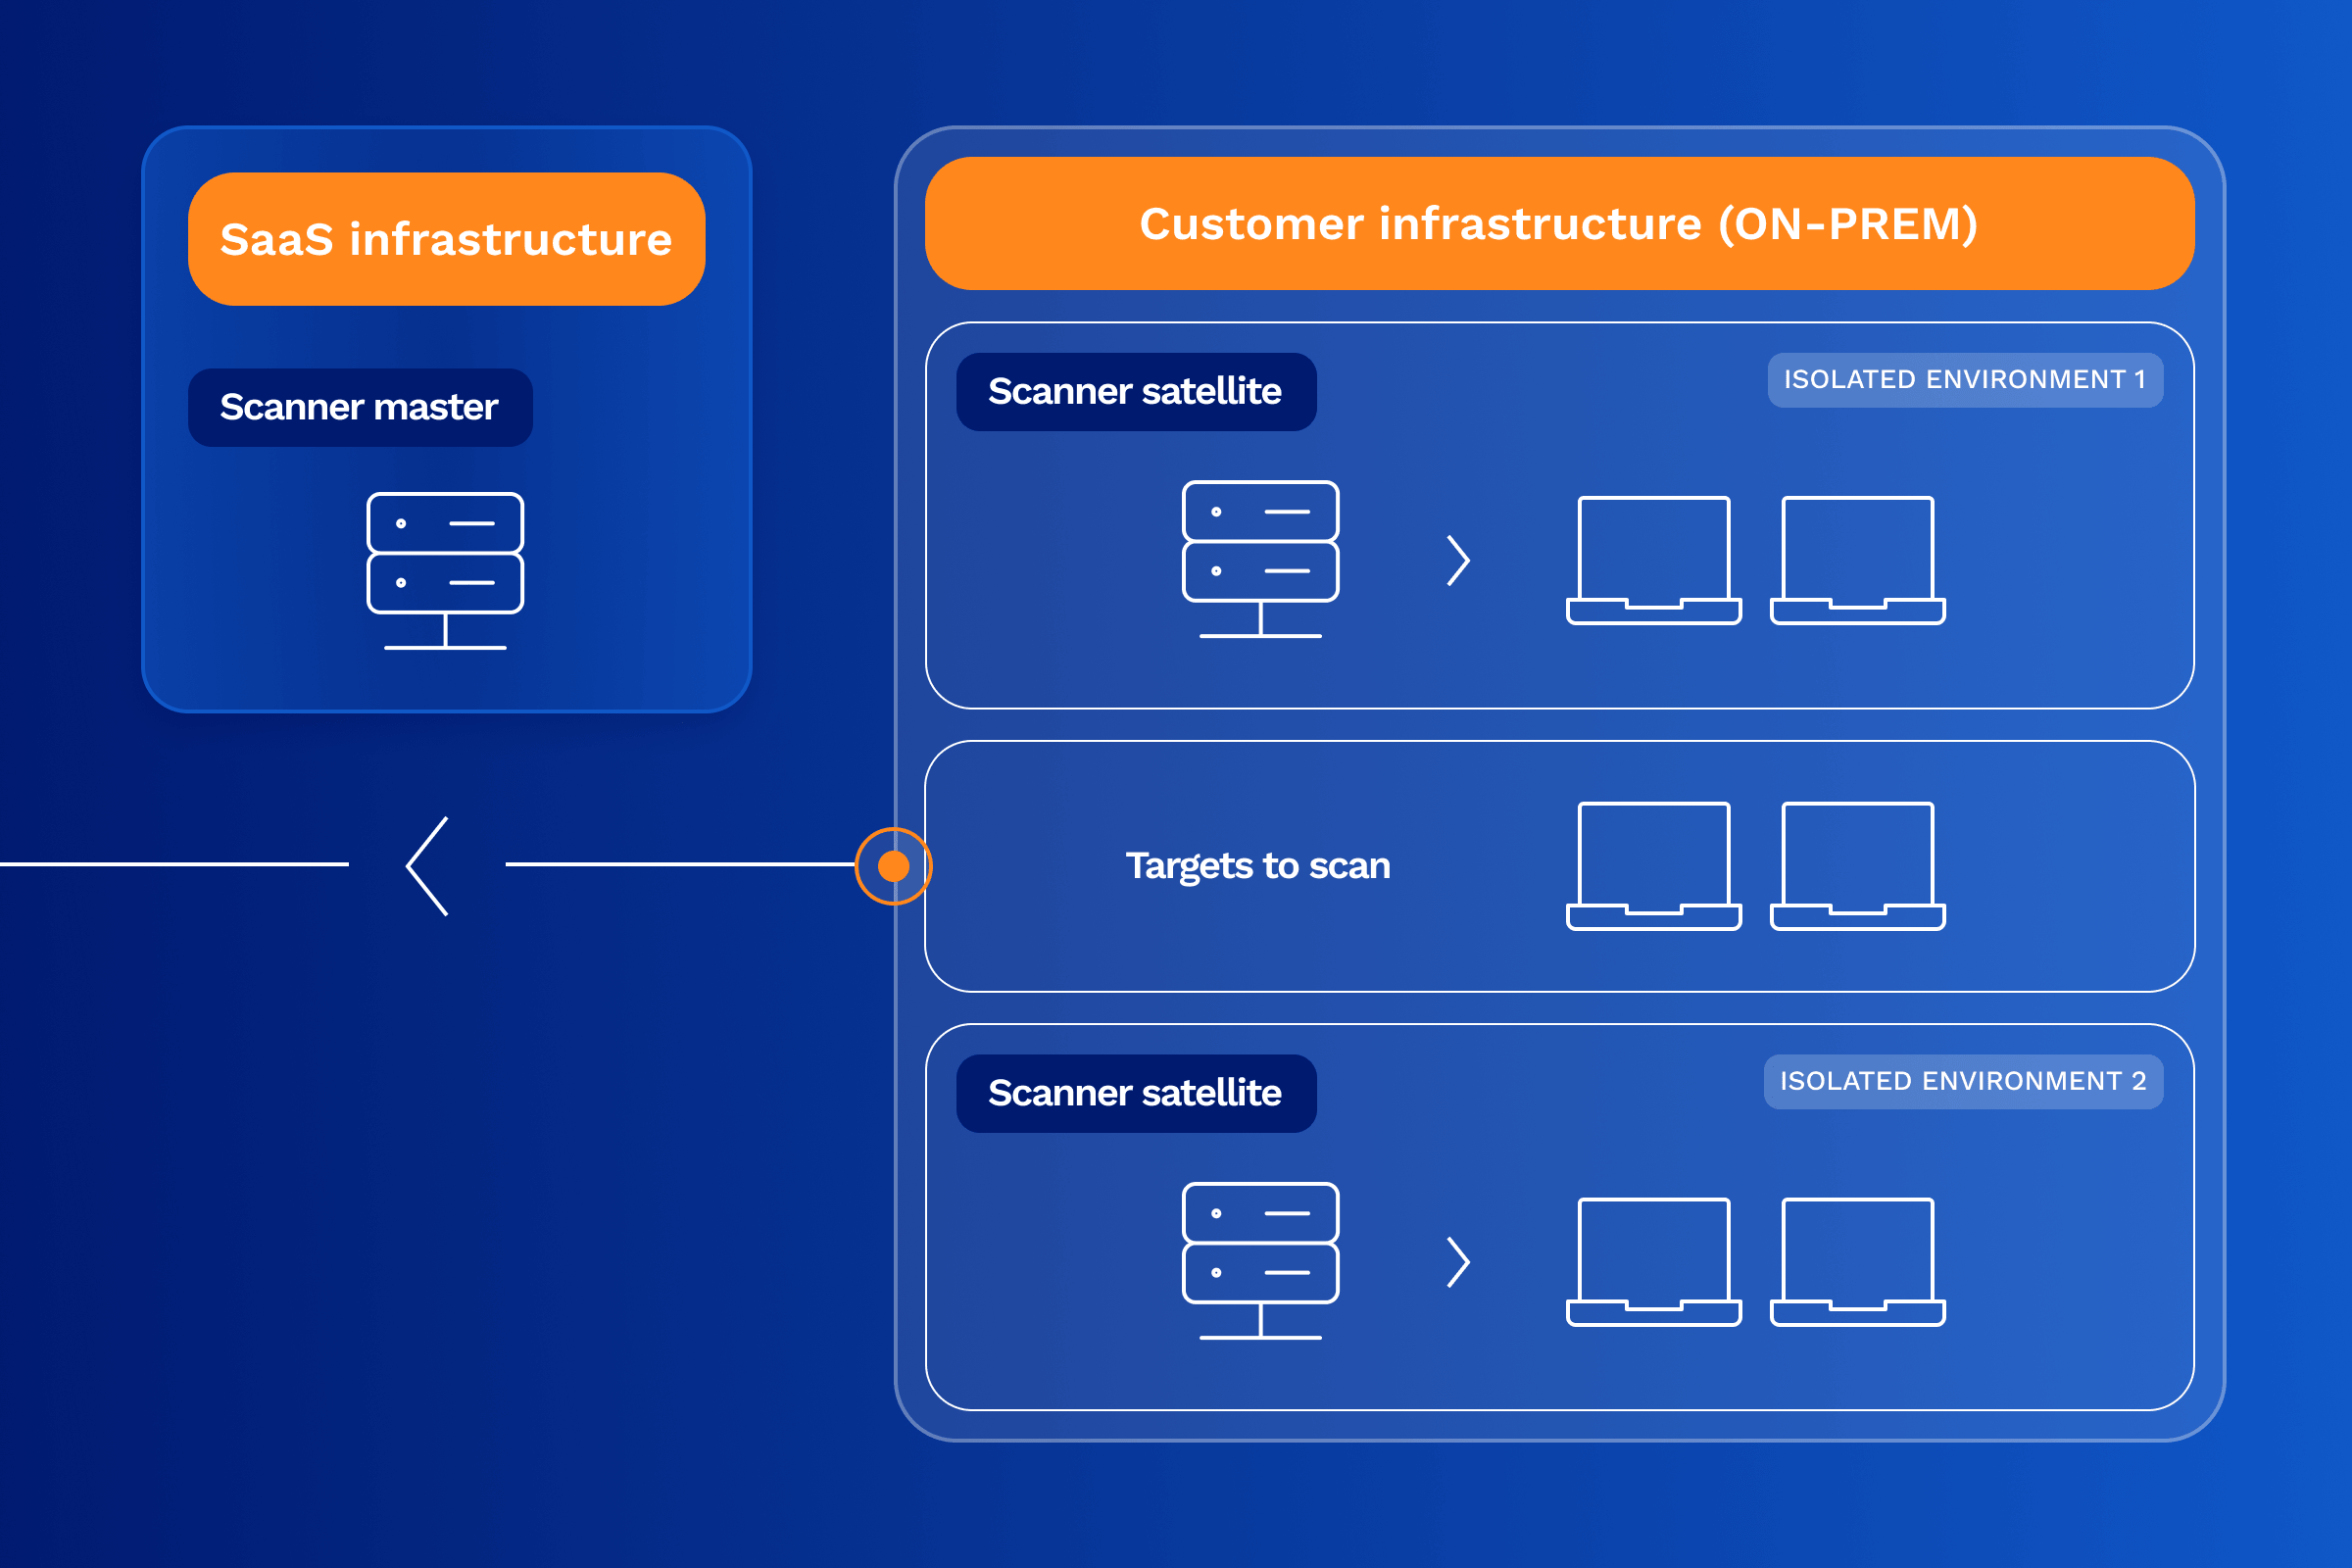
Master/satellite architecture
Deploy distributed scanners across segmented networks with encrypted synchronization
- Item 1
- Item 2
- Item 3
Local audit trails
Reports, logs, and dashboards generated entirely on-premises
- Item 1
- Item 2
- Item 3
subsystems
Sensitive subsystems
Retrieve security data without installing anything on your critical assets
For systems where installing an agent or scanner is not an option (industrial controllers, security equipment, or nuclear and critical infrastructure environments), Cyberwatch offers data collection via remote scripts or manual import. Information is then sent to a central console for analysis and reporting.
Lightweight scripts (PowerShell, Bash)
Executed on an ad-hoc basis on isolated systems, without permanent installation
- Item 1
- Item 2
- Item 3
Central console reporting
Results are consolidated in Cyberwatch for correlation, prioritization, and unified reporting
- Item 1
- Item 2
- Item 3
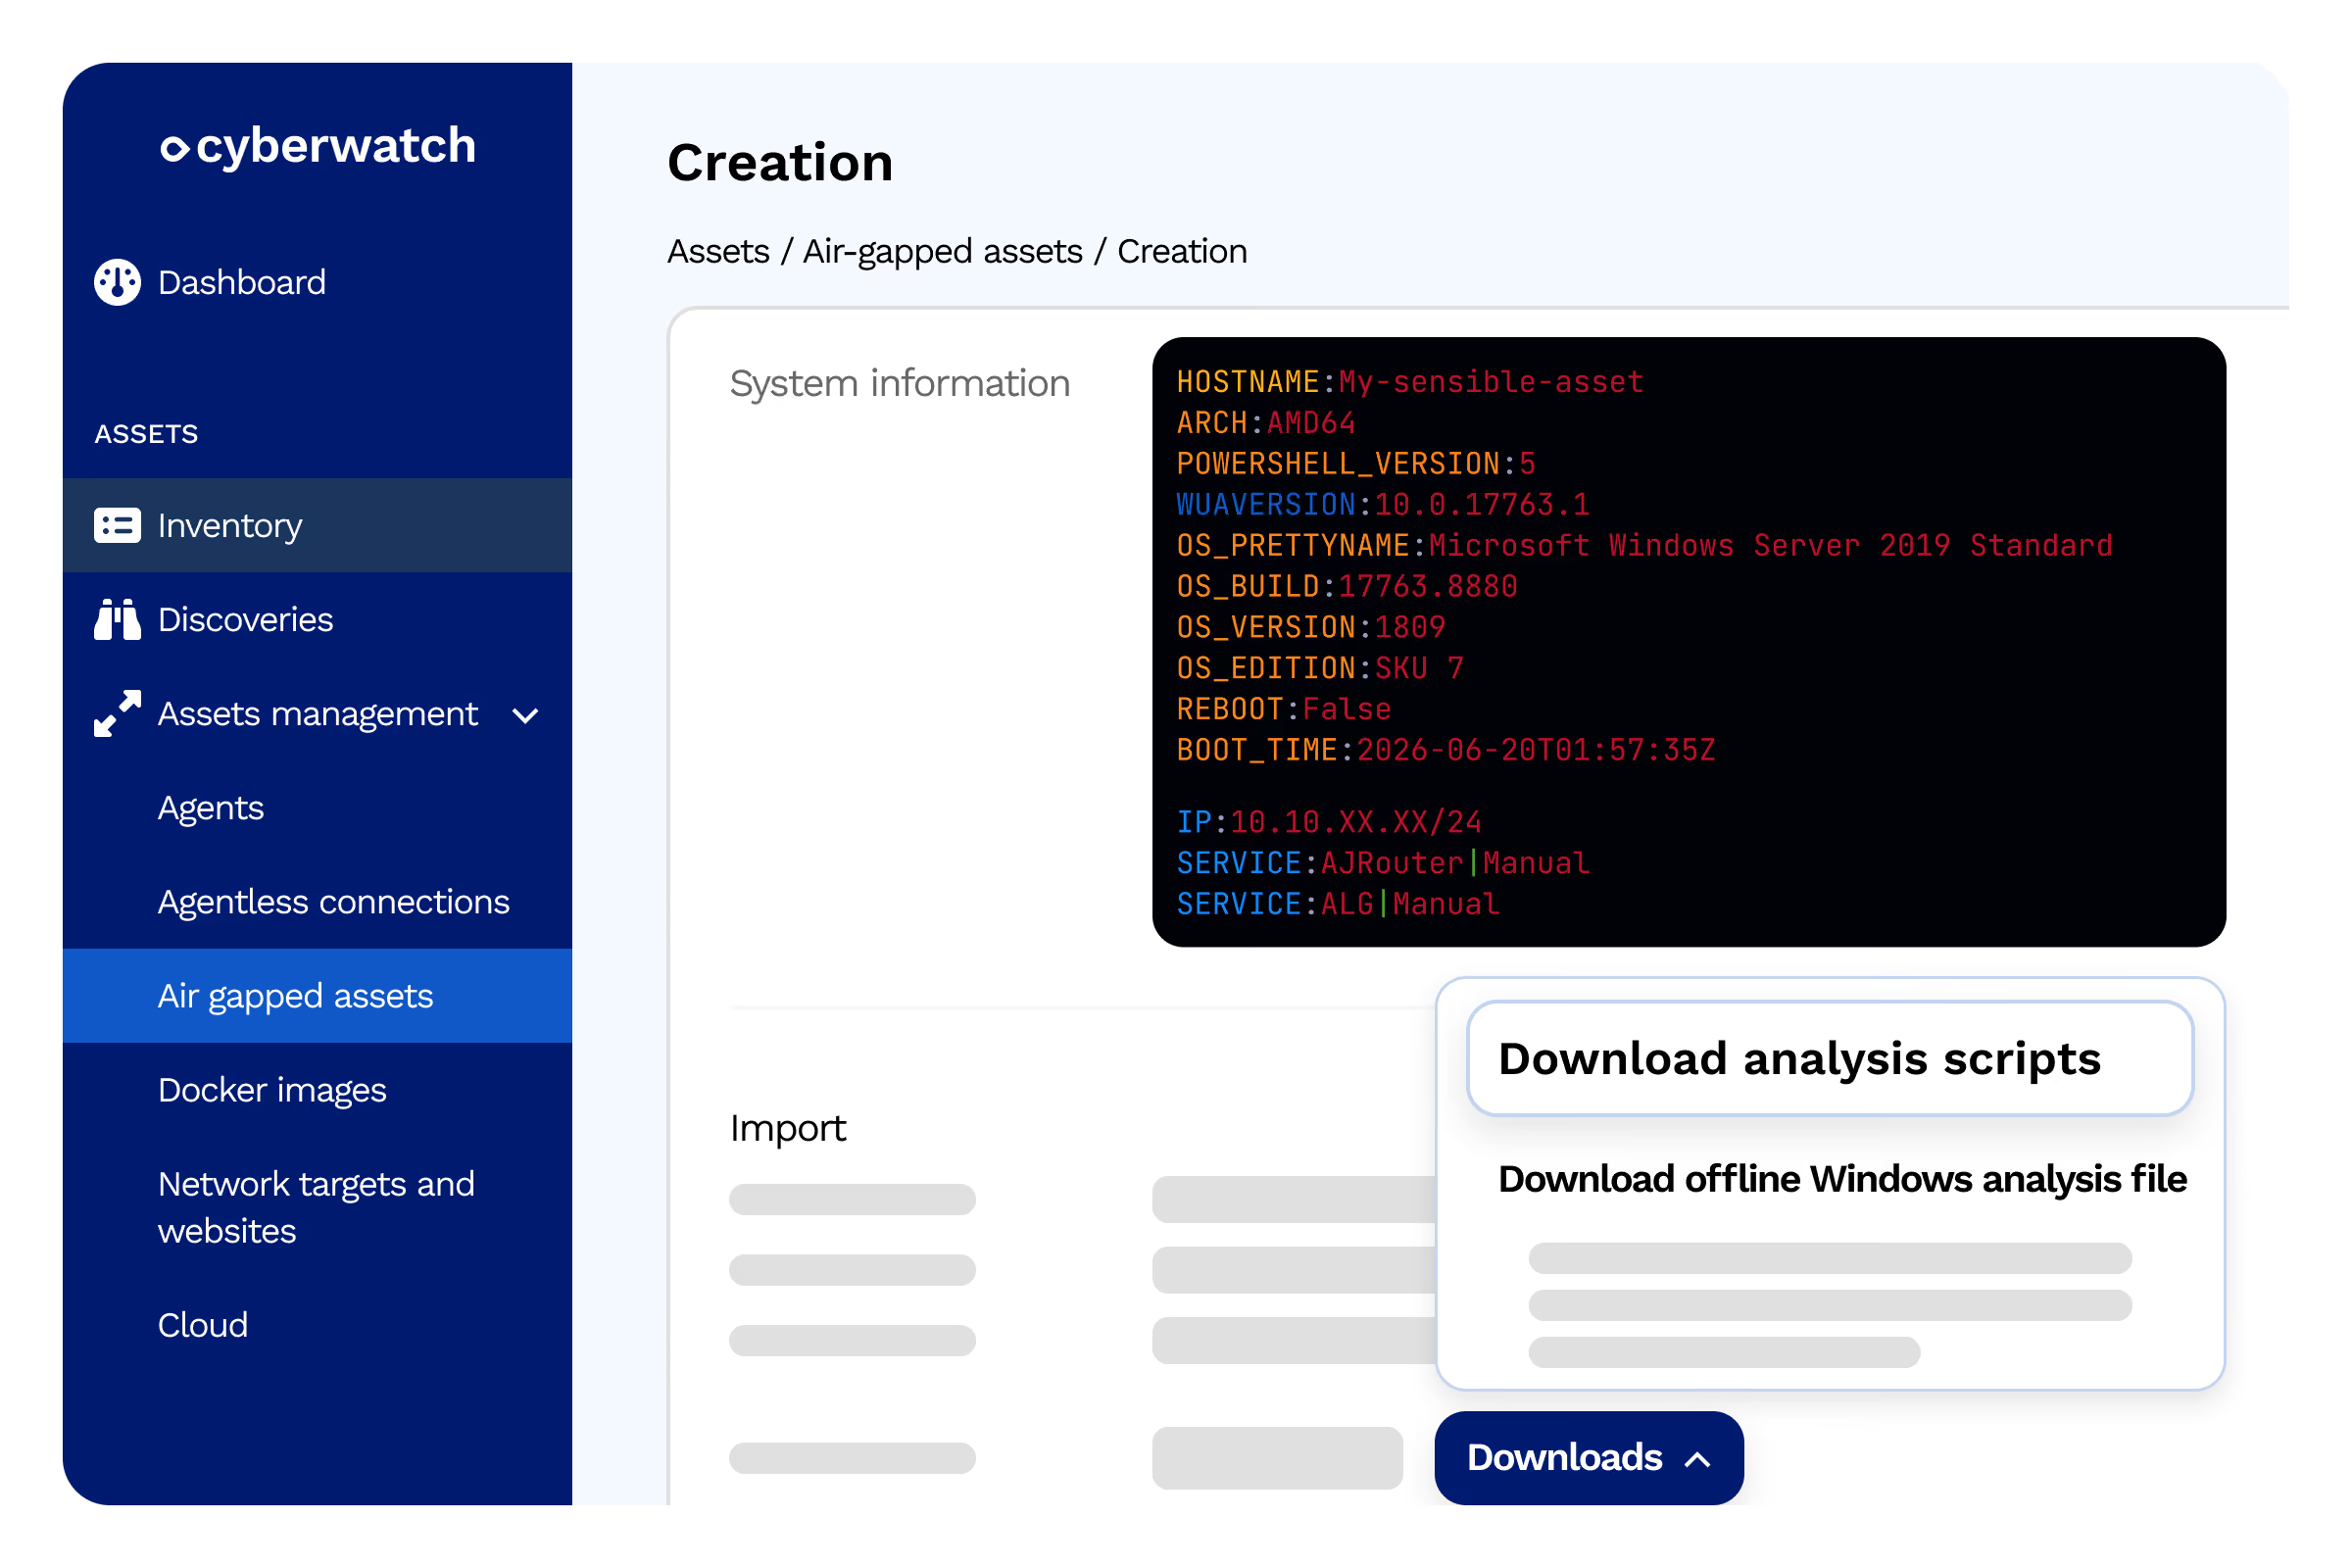
Manual CSV/JSON import
For assets that are completely disconnected or subject to authorization procedures
- Item 1
- Item 2
- Item 3
OT and regulated environments
Adapted to the constraints of industrial PLCs, nuclear safety systems, fire safety systems (SSI), and environments requiring specific compliance
- Item 1
- Item 2
- Item 3
on-premises
On-premises mode
Our primary, full-featured version, deployed within your infrastructure
The on-premises mode is the traditional deployment method most used by our clients. Cyberwatch is installed in your datacenter with all features included. You maintain full control over operations, data, and platform security.
Operational control
You decide on updates, scan windows, and retention policies
- Item 1
- Item 2
- Item 3
Data control
Your vulnerability data never leaves your infrastructure
- Item 1
- Item 2
- Item 3
Security control
Integration with your existing network architecture, firewall rules, and access policies
- Item 1
- Item 2
- Item 3
Full features
All Cyberwatch capabilities available: scans, compliance, patch management, SBOM, reporting, API
- Item 1
- Item 2
- Item 3
saas
SaaS mode on sovereign cloud
Even in SaaS, your data remains on a sovereign cloud
For organizations that want a managed deployment without having to handle the infrastructure, Cyberwatch offers a SaaS solution hosted exclusively on French and European sovereign clouds. No data is exposed to extraterritorial jurisdictions.
OVHcloud
French sovereign hosting, data centers in France
- Rockwell Automation— ControlLogix, CompactLogix, MicroLogix (via EtherNet/IP)
- Schneider Electric— Modicon M340, M580, Premium, Quantum (via Modbus TCP)
- Siemens— SIMATIC S7-300, S7-400, S7-1200, S7-1500 (via S7 protocol)
SecNumCloud-qualified clouds
For entities subject to the strictest ANSSI requirements
- Rockwell Automation— ControlLogix, CompactLogix, MicroLogix (via EtherNet/IP)
- Schneider Electric— Modicon M340, M580, Premium, Quantum (via Modbus TCP)
- Siemens— SIMATIC S7-300, S7-400, S7-1200, S7-1500 (via S7 protocol)
S3NS / Bleu
Clouds regulated under European law, operated by French providers
- Rockwell Automation— ControlLogix, CompactLogix, MicroLogix (via EtherNet/IP)
- Schneider Electric— Modicon M340, M580, Premium, Quantum (via Modbus TCP)
- Siemens— SIMATIC S7-300, S7-400, S7-1200, S7-1500 (via S7 protocol)
Legal guarantee
Not subject to the Cloud Act or FISA; data exclusively under French law
- Rockwell Automation— ControlLogix, CompactLogix, MicroLogix (via EtherNet/IP)
- Schneider Electric— Modicon M340, M580, Premium, Quantum (via Modbus TCP)
- Siemens— SIMATIC S7-300, S7-400, S7-1200, S7-1500 (via S7 protocol)
Nozomi Networks
Inventory import from Nozomi probes already deployed on your industrial networks
- Item 1
- Item 2
- Item 3
Allentis (Framatome subsidiary)
Native connector for Allentis NDR probes, ANSSI-qualified, for unified IT/OT mapping
- Item 1
- Item 2
- Item 3
Seckiot
Integration with Seckiot probes to enrich the OT inventory
- Item 1
- Item 2
- Item 3
Seckiot
Correlation between network data (probes) and system data (Safe Query) for a complete and deduplicated inventory
- Item 1
- Item 2
- Item 3
Testimonials
Pouvoir déployer une console complète isolée d'Internet, avec mise à jour manuelle de la base de vulnérabilités, était un prérequis pour certains de nos environnements les plus critiques.

Exemple à remplacer — Responsable sécurité, secteur public
Responsable sécurité des systèmes d'information

Le mode air-gap totalement déconnecté correspond exactement à nos exigences de sécurité pour les systèmes les plus sensibles, sans compromis sur la qualité de la détection.
Exemple à remplacer — Responsable SSI, défense
Responsable de la sécurité des systèmes d'information